Pre-Winter Special Sale - 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: spcl70

Practice Free 300-710 Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Exam Questions Answers With Explanation

We at Crack4sure are committed to giving students who are preparing for the Cisco 300-710 Exam the most current and reliable questions . To help people study, we've made some of our Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 exam materials available for free to everyone. You can take the Free 300-710 Practice Test as many times as you want. The answers to the practice questions are given, and each answer is explained.

Question # 6

When packet capture is used on a Cisco Secure Firewall Threat Defense device and the packet flow is wailing on the malware query, which Snort verdict appears?

A.

retry

B.

replace

C.

block

D.

blocfcflow

Question # 7

Which communication is blocked from the bridge groups when multiple are configured in transparent mode on a Cisco Secure Firewall Threat Defense appliance?

A.

With client devices

B.

With other routers

C.

With each other

D.

With the internet

Question # 8

What is a method used by Cisco Rapid Threat Containment to contain the threat in the network?

A.

change of authentication

B.

share context data

C.

TACACS+

D.

trustsec segmentation

Question # 9

On the advanced tab under inline set properties, which allows interfaces to emulate a passive interface?

A.

transparent inline mode

B.

TAP mode

C.

strict TCP enforcement

D.

propagate link state

Question # 10

An engineer must define a URL object on Cisco FMC. What is the correct method to specify the URL without performing SSL inspection?

A.

Use Subject Common Name value.

B.

Specify all subdomains in the object group.

C.

Specify the protocol in the object.

D.

Include all URLs from CRL Distribution Points.

Question # 11

An engineer is configuring a second Cisco FMC as a standby device but is unable to register with the active unit. What is causing this issue?

A.

The primary FMC currently has devices connected to it.

B.

The code versions running on the Cisco FMC devices are different

C.

The licensing purchased does not include high availability

D.

There is only 10 Mbps of bandwidth between the two devices.

Question # 12

An engineer has been tasked with providing disaster recovery for an organization ' s primary Cisco FMC. What must be done on the primary and secondary Cisco FMCs to ensure that a copy of the original corporate policy is available if the primary Cisco FMC fails?

A.

Configure high-availability in both the primary and secondary Cisco FMCs

B.

Connect the primary and secondary Cisco FMC devices with Category 6 cables of not more than 10 meters in length.

C.

Place the active Cisco FMC device on the same trusted management network as the standby device

D.

Restore the primary Cisco FMC backup configuration to the secondary Cisco FMC device when the primary device fails

Question # 13

A network administrator is trying to convert from LDAP to LDAPS for VPN user authentication on a Cisco FTD. Which action must be taken on the Cisco FTD objects to accomplish this task?

A.

Add a Key Chain object to acquire the LDAPS certificate.

B.

Create a Certificate Enrollment object to get the LDAPS certificate needed.

C.

Identify the LDAPS cipher suite and use a Cipher Suite List object to define the Cisco FTD connection requirements.

D.

Modify the Policy List object to define the session requirements for LDAPS.

Question # 14

Network users are experiencing Intermittent issues with internet access. An engineer ident med mat the issue Is being caused by NAT exhaustion. How must the engineer change the dynamic NAT configuration to provide internet access for more users without running out of resources?

A.

Define an additional static NAT for the network object in use.

B.

Configure fallthrough to interface PAT on ' he Advanced tab.

C.

Convert the dynamic auto NAT rule to dynamic manual NAT.

D.

Add an identity NAT rule to handle the overflow of users.

Question # 15

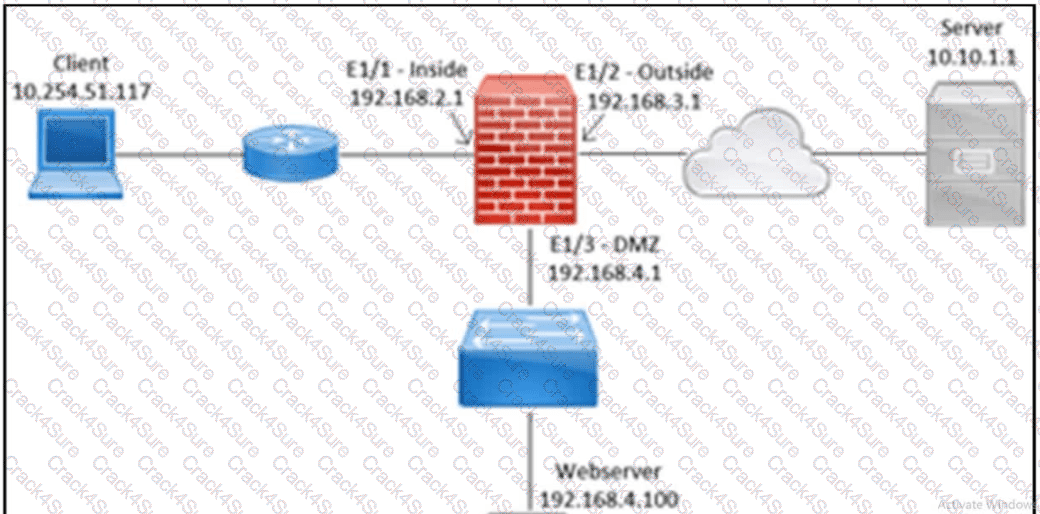
Refer to the exhibit.

300-710 question answer

A client with IP address 10.254.51.117 connects through a Cisco Secure Firewall Threat Defense device toward a website at 10.10.1.1. The packet capture shows repeated TCP SYN packets from the client without completion of the three-way handshake. Which action must the engineer take to resolve the issue?

A.

Configure the inside interface to send ACK messages.

B.

Add a firewall rule that allows the web server to communicate with the DMZ.

C.

Add a firewall rule that allows ACK responses from the inside to the outside.

D.

Configure the outside interface to receive SYN-ACK messages.

Question # 16

An organization is installing a new Cisco FTD appliance in the network. An engineer is tasked with configuring access between two network segments within the same IP subnet. Which step is needed to accomplish this task?

A.

Assign an IP address to the Bridge Virtual Interface.

B.

Permit BPDU packets to prevent loops.

C.

Specify a name for the bridge group.

D.

Add a separate bridge group for each segment.

Question # 17

An engineer must change the mode of a Cisco Secure Firewall Threat Defense (FTD) firewall in the Cisco Secure Firewall Management Center (FMC) inventory. The engineer must take these actions:

• Register Secure FTD with Secure FMC.

• Change the firewall mode.

• Deregister the Secure FTD device from Secure FMC.

How must the engineer take FTD take the actions?

A.

Reload the Secure FTD device.

B.

Configure the management IP address.

C.

Access the Secure FTD CLI from the console port.

D.

Erase the Secure FTD configuration

Question # 18

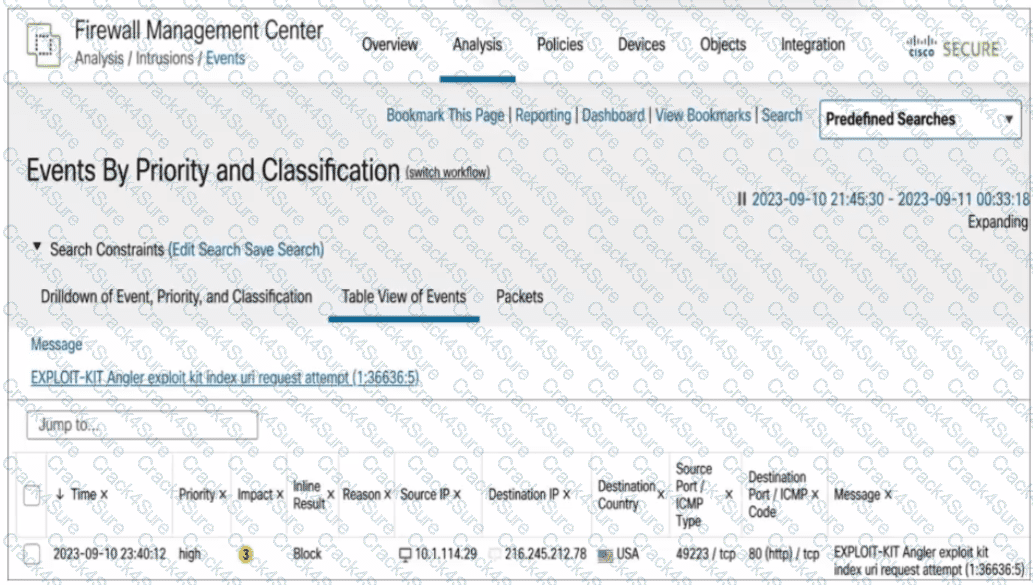
Refer to the exhibit.

300-710 question answer

An engineer is analyzing an event in Cisco Secure Firewall Management Center Considering this log entry, which specific security threat is observed?

A.

information leak

B.

privilege escalation

C.

denial of service

D.

memory exhaustion

Question # 19

What is a behavior of a Cisco FMC database purge?

A.

User login and history data are removed from the database if the User Activity check box is selected.

B.

Data can be recovered from the device.

C.

The appropriate process is restarted.

D.

The specified data is removed from Cisco FMC and kept for two weeks.

Question # 20

An engineer wants to convert a Cisco Secure Firewall Threat Defense device that is currently managed by Cisco Secure Firewall Management Center from routed mode to transparent mode. Which CLI command must the engineer execute first to perform this conversion?

A.

no configure manager

B.

no configure firewall routed

C.

configure manager delete

D.

configure firewall transparent

Question # 21

An engineer is investigating connectivity problems on Cisco Firepower that is using service group tags. Specific devices are not being tagged correctly, which is preventing clients from using the proper policies when going through the firewall How is this issue resolved?

A.

Use traceroute with advanced options.

B.

Use Wireshark with an IP subnet filter.

C.

Use a packet capture with match criteria.

D.

Use a packet sniffer with correct filtering

Question # 22

A security engineer must configure a Cisco FTD appliance to inspect traffic coming from the internet. The Internet traffic will be mirrored from the Cisco Catalyst 9300 Switch. Which configuration accomplishes the task?

A.

Set interface configuration mode to none.

B.

Set the firewall mode to transparent.

C.

Set the firewall mode to routed.

D.

Set interface configuration mode to passive.

Question # 23

Network traffic coining from an organization ' s CEO must never be denied. Which access control policy configuration option should be used if the deployment engineer is not permitted to create a rule to allow all traffic?

A.

Configure firewall bypass.

B.

Change the intrusion policy from security to balance.

C.

Configure a trust policy for the CEO.

D.

Create a NAT policy just for the CEO.

Question # 24

A network administrator configured a NAT policy that translates a public IP address to an internal web server IP address. An access policy has also been created that allows any source to reach the public IP address on port 80. The web server is still not reachable from the Internet on port 80. Which configuration change is needed?

A.

The intrusion policy must be disabled for port 80.

B.

The access policy rule must be configured for the action trust.

C.

The NAT policy must be modified to translate the source IP address as well as destination IP address.

D.

The access policy must allow traffic to the internal web server IP address.

Question # 25

An engineer must configure high availability for the Cisco Firepower devices. The current network topology does not allow for two devices to pass traffic concurrently. How must the devices be implemented in this environment?

A.

in active/active mode

B.

in a cluster span EtherChannel

C.

in active/passive mode

D.

in cluster interface mode

Question # 26

A security administrator must configure Cisco Secure Firewall Management Center so that certain intrusion rules are active only during specified times. Which action must the administrator take?

A.

Assign a time range directly to every intrusion rule in the intrusion policy.

B.

Configure a time-based trigger in the intrusion policy to enable the rules at defined times.

C.

Create time-based access control rules that apply the intrusion policy at the scheduled intervals.

D.

Create a scheduled task that activates and deactivates the intrusion rules at the required times.

Question # 27

An engineer must integrate a third-party security intelligence feed with Cisco Secure Firewall Management Center. Secure Firewall Management Center is running Version 6.2.3 and has 8

GB of memory. Which two actions must be taken to implement Threat Intelligence Director? (Choose two.)

A.

Enable REST API access.

B.

Add a TAXII server.

C.

Add the URL of the TAXII server.

D.

Upgrade to version 6.6.

E.

Add 7 GB of memory.

Question # 28

An engineer plans to reconfigure an existing Cisco FTD from transparent mode to routed mode. Which additional action must be taken to maintain communication Between me two network segments?

A.

Configure a NAT rule so mat traffic between the segments is exempt from NAT.

B.

Update the IP addressing so that each segment is a unique IP subnet.

C.

Deploy inbound ACLs on each interface to allow traffic between the segments.

D.

Assign a unique VLAN ID for the interface in each segment.

Question # 29

An engineer is investigating connectivity problems on Cisco Firepower for a specific SGT. Which command allows the engineer to capture real packets that pass through the firewall using an SGT of 64?

A.

capture CAP type inline-tag 64 match ip any any

B.

capture CAP match 64 type inline-tag ip any any

C.

capture CAP headers-only type inline-tag 64 match ip any any

D.

capture CAP buffer 64 match ip any any

Question # 30

A network engineer is implementing high availability between two Cisco Secure Firewall Threat Defense devices. The engineer already checked the model, version, and number of interfaces Which two configurations must the engineer match next to meet the requirement? (Choose two.)

A.

devices must have the same hostname for both chassis

B.

type of interfaces that are on the devices

C.

domains the devices are in must match

D.

devices must be in a different firewall mode

E.

devices must have an identical NTP configuration

Question # 31

An engineer must integrate a thud-party security Intelligence teed with Cisco Secure Firewall Management Center. Secure Firewall Management Center is running Version 6.2 3 and has 8 GB of memory. Which two actions must be taken to implement Throat Intelligence Director? (Choose two.)

A.

Upgrade to version 6.6.

B.

Enable REST API access.

C.

Add the URL of the TAXII server.

D.

Add 7 GB of memory.

E.

Add a TAXII server

Question # 32

What is the difference between inline and inline tap on Cisco Firepower?

A.

Inline tap mode can send a copy of the traffic to another device.

B.

Inline tap mode does full packet capture.

C.

Inline mode cannot do SSL decryption.

D.

Inline mode can drop malicious traffic.

Question # 33

Which two conditions are necessary for high availability to function between two Cisco FTD devices? (Choose two.)

A.

The units must be the same version

B.

Both devices can be part of a different group that must be in the same domain when configured within the FMC.

C.

The units must be different models if they are part of the same series.

D.

The units must be configured only for firewall routed mode.

E.

The units must be the same model.

Question # 34

Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session. Which action must the engineer take to resolve the issue?

A.

Forward the captured data lo an FTP server

B.

Increase the amount of RAM allocated for the capture.

C.

Provide a file name to save the data.

D.

Ensure that the allocated memory is sufficient.

Question # 35

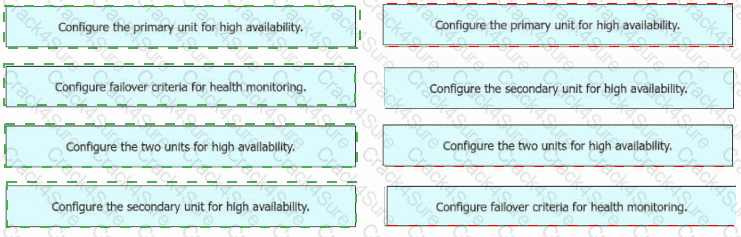
An engineer must configure high availability on two Cisco Secure Firewall Threat Defense appliances. Drag and drop the configuration steps from the left into the sequence on the right.
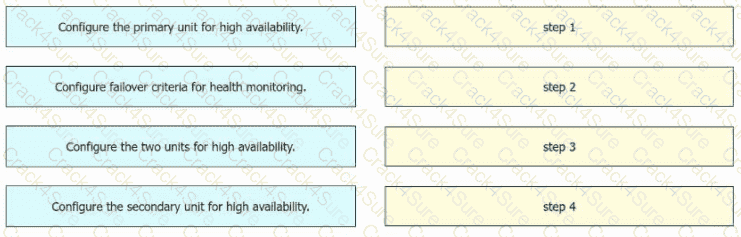
300-710 question answer

Question # 36

A network administrator manages a network with multiple firewalls in a datacenter using Cisco Secure Firepower Management Center. The administrator must change a next-generation firewall from routed to transparent mode. Which action must the administrator take next to meet the requirement?

A.

Deregister the firewall in Cisco Secure Firewall Management Center.

B.

Enter the configure transparent firewall command from the CLI.

C.

Create one or more bridge groups from the CLI.

D.

Manually delete the interface configuration from the CLI.

Question # 37

Which Cisco Secure Firewall Threat Defense interface mode must be deployed when implementing an IPS that uses a SPAN port for traffic monitoring?

A.

Routed

B.

Passive

C.

Transparent

D.

Inline

Question # 38

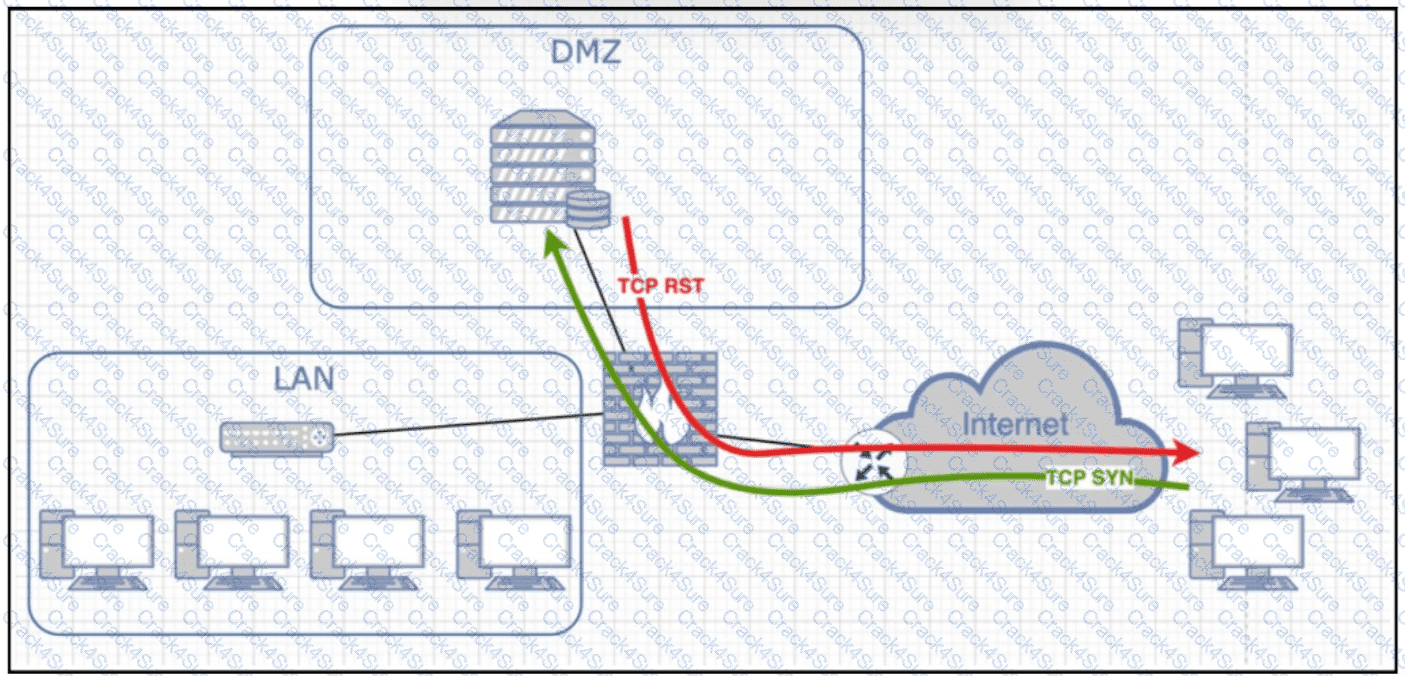
Refer to the exhibit.

300-710 question answer

Following a critical incident, an engineer must determine why a server in the DMZ is sending TCP RST responses. Internet users can access the application but cannot view its main webpage. Where must the engineer capture the traffic to identify and resolve the issue?

A.

Internet-facing interface of the perimeter firewall

B.

Inside interface of the perimeter router

C.

Router of the ISP

D.

DMZ interface of the perimeter firewall

Question # 39

An engineer must investigate a connectivity issue and decides to use the packet capture feature on Cisco FTD. The goal is to see the real packet going through the Cisco FTD device and see the Snort detection actions as a part of the output. After the capture-traffic command is issued, only the packets are displayed. Which action resolves this issue?

A.

Use the verbose option as a part of the capture-traffic command

B.

Use the capture command and specify the trace option to get the required information.

C.

Specify the trace using the -T option after the capture-traffic command.

D.

Perform the trace within the Cisco FMC GUI instead of the Cisco FTD CLI.

Question # 40

After a network security breach, an engineer must strengthen the security of the corporate network. Upper management must be regularly updated with a high-level overview of any

occurring network threats. Which access must the engineer provide upper management to view the required data from Cisco Secure Firewall Management Center?

A.

Analysis > Status with a sliding time window of one day

B.

Events by priority and classification and set a sliding time window of one day

C.

Reports with a daily recurring task that generates based on the network risk report template

D.

Security Intelligence Statistics dashboard set to Show the Last option to one day

Question # 41

An organization does not want to use the default Cisco Firepower block page when blocking HTTP traffic. The organization wants to include information about its policies and procedures to help educate the users whenever a block occurs. Which two steps must be taken to meet these requirements? (Choose two.)

A.

Modify the system-provided block page result using Python.

B.

Create HTML code with the information for the policies and procedures.

C.

Edit the HTTP request handling in the access control policy to customized block.

D.

Write CSS code with the information for the policies and procedures.

E.

Change the HTTP response in the access control policy to custom.

Question # 42

A network administrator has converted a Cisco FTD from using LDAP to LDAPS for VPN authentication. The Cisco FMC can connect to the LDAPS server, but the Cisco FTD is not connecting. Which configuration must be enabled on the Cisco FTD?

A.

SSL must be set to a use TLSv1.2 or lower.

B.

The LDAPS must be allowed through the access control policy.

C.

DNS servers must be defined for name resolution.

D.

The RADIUS server must be defined.

Question # 43

A network administrator reviews me attack risk report and notices several Low-Impact attacks. What does this type of attack indicate?

A.

All attacks are listed as low until manually categorized.

B.

The host is not vulnerable to those attacks.

C.

The attacks are not dangerous to the network.

D.

The host is not within the administrator ' s environment.

Question # 44

Upon detecting a flagrant threat on an endpoint, which two technologies instruct Cisco Identity Services Engine to contain the infected endpoint either manually or automatically? (Choose two.)

A.

Cisco ASA 5500 Series

B.

Cisco FMC

C.

Cisco AMP

D.

Cisco Stealthwatch

E.

Cisco ASR 7200 Series

Question # 45

A security engineer wants to add the Interface Traffic widget to the Summary Dashboard in Cisco Secure Firewall Management Center. The engineer clicks Add Widgets and enters edit mode. Which set of actions must the security engineer take to complete the configuration?
A.

Click All Categories, open the Analysis & Reporting tab, and then click the Add widget button.

B.

Click All Categories, open the New tab, and then click the Add widget button.

C.

Click All Categories, open the Operations tab, and then click the Add widget button.

D.

Click All Categories, open the Miscellaneous tab, and then click the Add widget button.

Question # 46

300-710 question answer

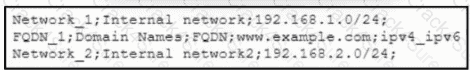
Refer to the exhibit. An engineer must import three network objects into the Cisco Secure Firewall Management Center by using a CSV file. Which header must be configured in the CSV file to accomplish the task?

A.

NAME;DESCRIPTION;TYPE;VALUE;LOOKUP;

B.

Name; Description; Type;Value;Lookup;

C.

Name; Description; Type;Value;DN;

D.

NAME;DESCRIPTION; TYPE;VALUE;DN;

Question # 47

Which limitation applies to Cisco Firepower Management Center dashboards in a multidomain environment?

A.

Child domains can view but not edit dashboards that originate from an ancestor domain.

B.

Child domains have access to only a limited set of widgets from ancestor domains.

C.

Only the administrator of the top ancestor domain can view dashboards.

D.

Child domains cannot view dashboards that originate from an ancestor domain.

Question # 48

An administrator must fix a network problem whereby traffic from the inside network to a webserver is not getting through an instance of Cisco Secure Firewall Threat Defense. Which command must the administrator use to capture packets to the webserver that are dropped by Secure Firewall Throat Defense and resold the issue?

A.

capture CAP int OUTSIDE match ip any host WEBSERVERIP

B.

capture CAP type asp-drop all headers-only

C.

capture CAP int INSIDE match ip any host WEBSERVERIP

D.

capture CAP int INSIDE match tcp any 80 host WEBSERVERlP 80

Question # 49

An organization has a Cisco IPS running in inline mode and is inspecting traffic for malicious activity. When traffic is received by the Cisco IRS, if it is not dropped, how does the traffic get to its destination?

A.

It is retransmitted from the Cisco IPS inline set.

B.

The packets are duplicated and a copy is sent to the destination.

C.

It is transmitted out of the Cisco IPS outside interface.

D.

It is routed back to the Cisco ASA interfaces for transmission.

Question # 50

An engineer is configuring URL filtering tor a Cisco Secure Firewall Threat Defense device in Cisco Secure Firewall Management Centre. Use ' s must receive a warning when they access

..wwww badaduitsito com with the option of continuing to the website if they choose to No other websites should he blocked. Which two actions must the engineer take to moot these requirements?

A.

Configure an access control rule that matches an URL object for http://www.Dadadullsile.com ' and set the action to Interactive Block.

B.

On the HTTP Responses tab of the access control policy editor, set the Interactive Block Response Page to System-provided.

C.

Configure the default action for the access control policy to Interactive Block.

D.

On the HTTP Responses tab of the access control policy editor set the Block Response Page to Custom.

E.

Configure an access control rule that matches the Adult URL category and sot the action to Interactive Block

Question # 51

Which Cisco Firepower rule action displays an HTTP warning page?

A.

Monitor

B.

Block

C.

Interactive Block

D.

Allow with Warning

Question # 52

A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?

A.

The destination MAC address is optional if a VLAN ID value is entered

B.

Only the UDP packet type is supported

C.

The output format option for the packet logs unavailable

D.

The VLAN ID and destination MAC address are optional

Question # 53

What is the purpose of the IRB feature in next-generation firewall?

A.

To allow multiple physical interfaces to be part of the same VLAN

B.

To enable transparent bridging between two Layer 2 interfaces

C.

To block routing between two Layer 3 interfaces

D.

To configure NAT in transparent mode

Question # 54

Which command is entered in the Cisco FMC CLI to generate a troubleshooting file?

A.

show running-config

B.

show tech-support chassis

C.

system support diagnostic-cli

D.

sudo sf_troubleshoot.pl

Question # 55

A consultant Is working on a project where the customer is upgrading from a single Cisco Firepower 2130 managed by FDM to a pair of Cisco Firepower 2130s managed oy FMC tor nigh availability. The customer wants the configures of the existing device being managed by FDM to be carried over to FMC and then replicated to the additional: device being added to create the high availability pair. Which action must the consultant take to meet this requirement?

A.

The current FDM configuration must be configured by hand into FMC before the devices are registered.

B.

The current FDM configuration will be converted automatically into FMC when the device registers.

C.

The current FDM configuration must be migrated to FMC using the Secure Firewall Migration Tool.

D.

The FTD configuration must be converted to ASA command format, which can then be migrated to FMC.

Question # 56

What is the result when two users modify a VPN policy at the same lime on a Cisco Secure Firewall Management Center managed device?

A.

Both users can edit the policy arid the last saved configuration persists.

B.

The first user locks the configuration when selecting edit on the policy.

C.

The changes from both users will be merged together into the policy.

D.

The system prevents modifications to the policy by multiple users.

Question # 57

Which feature sets up multiple interfaces on a Cisco Secure Firewall Threat Defense to be on the same subnet?

A.

EtherChannel

B.

SVI

C.

BVI

D.

security levels

Question # 58

With a recent summer time change, system logs are showing activity that occurred to be an hour behind real time Which action should be taken to resolve this issue?
A.

Manually adjust the time to the correct hour on all managed devices

B.

Configure the system clock settings to use NTP with Daylight Savings checked

C.

Manually adjust the time to the correct hour on the Cisco FMC.

D.

Configure the system clock settings to use NTP

Question # 59

300-710 question answer

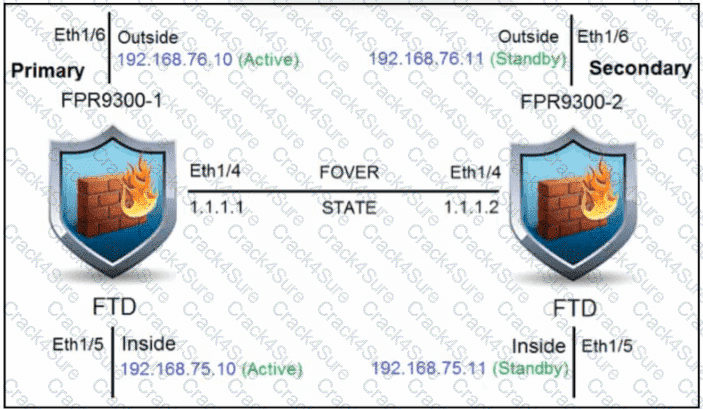
Refer to the exhibit. An engineer is configuring a high-availability solution that has the hardware devices and software versions:

two Cisco Secure Firewall 9300 Security Appliances with FXOS SW 2.0(1.23)

software Cisco Secure Firewall Threat Defense 6.0.1.1 (build 1023) on both appliances

one Cisco Secure Firewall Management Center with SW 6.0.1.1 (build 1023)

Which condition must be met to complete the high-availability configuration?

A.

DHCP must be configured on at least one firewall interface.

B.

The version numbers must have the same patch number.

C.

Both firewalls must have the same number of interfaces.

D.

Both firewalls must be in transparent mode.

Question # 60

A network administrator is trying to configure Active Directory authentication for VPN authentication to a Cisco Secure Firewall Threat Defence instance that is registered with Cisco Secure Firewall Management Center. Which system settings must be configured first in Secure Firewall Management Center to accomplish the goal?

A.

Device, Remote Access VPN

B.

System, Realms

C.

Policies, Authentication

D.

Authentication, Device

Question # 61

Which feature issupportedby IRB on Cisco FTD devices?
A.

redundant interface

B.

dynamic routing protocol

C.

EtherChannel interface

D.

high-availability cluster

Question # 62

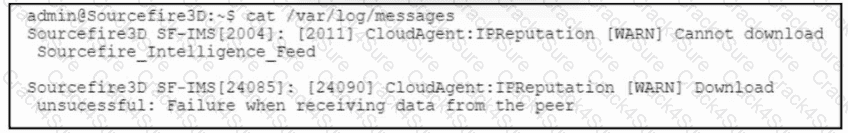
300-710 question answer

Refer to the exhibit. A Cisco Secure Firewall Management Center, 7.0 device fails to receive intelligence feed updates. The Cisco Secure Firewall Management Center is configured to use a proxy server that performs SSL inspection. Which action allows the Cisco Secure Firewall Management Center device to download the intelligence feed updates?

A.

Install a self-signed certificate on the proxy server for intelligence.sourcefire.com.

B.

Verify that the proxy server can use HTTPS to communicate to the internet.

C.

Ensure that proxy authentication is disabled for the Cisco Secure Firewall Management Center device.

D.

Bypass the proxy server for intelligence.sourcefire.com.

Question # 63

What is a benefit of implementing Integrated Routing and Bridging (IRB) on a Cisco Secure Firewall device?
A.

Multiple physical interfaces on the device can be on the same VLAN.

B.

Uptime is increased by preventing the device from being a single point of failure.

C.

Customers with different security policies can reside on the same device.

D.

Threat information can be dynamically updated from Cisco Talos.

Question # 64

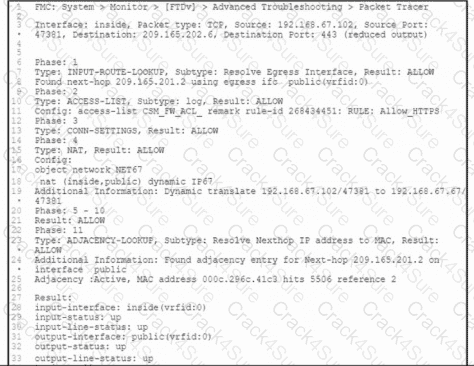
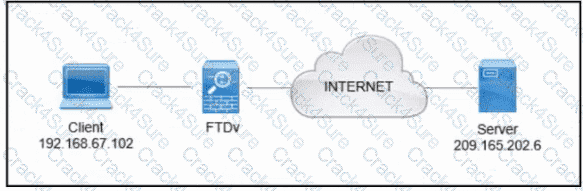
300-710 question answer

300-710 question answer

Refer to the exhibit. A client that has IP address 192.168.67.102 reports issues when connecting to a remote server. Based on the topology and output of packet tracer tool, which action resolves the connectivity issue?

A.

Add the route to the destination.

B.

Unblock the access rule on FTDv.

C.

Restart the client-side application.

D.

Reconfigure NAT on FTDv.

Question # 65

Which report template field format is available in Cisco FMC?

A.

box lever chart

B.

arrow chart

C.

bar chart

D.

benchmark chart

Question # 66

An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration tasks must be performed to achieve this file lookup? (Choose two).

A.

The Cisco FMC needs to include a SSL decryption policy.

B.

The Cisco FMC needs to connect to the Cisco AMP for Endpoints service.

C.

The Cisco FMC needs to connect to the Cisco ThreatGrid service directly for sandboxing.

D.

The Cisco FMC needs to connect with the FireAMP Cloud.

E.

The Cisco FMC needs to include a file inspection policy for malware lookup.

Question # 67

Which component is needed to perform rapid threat containment with Cisco FMC?

A.

ISE

B.

RESTful API

C.

SIEM

D.

DDI

Question # 68

A VPN user is unable to conned lo web resources behind the Cisco FTD device terminating the connection. While troubleshooting, the network administrator determines that the DNS responses are not getting through the Cisco FTD What must be done to address this issue while still utilizing Snort IPS rules?

A.

Uncheck the " Drop when Inline " box in the intrusion policy to allow the traffic.

B.

Modify the Snort rules to allow legitimate DNS traffic to the VPN users.

C.

Disable the intrusion rule threshes to optimize the Snort processing.

D.

Decrypt the packet after the VPN flow so the DNS queries are not inspected

Question # 69

An engineer installs a Cisco FTD device and wants to inspect traffic within the same subnet passing through a firewall and inspect traffic destined to the internet.

Which configuration will meet this requirement?

A.

transparent firewall mode with IRB only

B.

routed firewall mode with BVI and routed interfaces

C.

transparent firewall mode with multiple BVIs

D.

routed firewall mode with routed interfaces only

Question # 70

An engineer is configuring two new Cisco Secure Firewall Threat Defense appliances as a high-availability pair. The high-availability pair must detect a failure on the failover link and trigger failover more quickly. Which two settings must the engineer decrease? (Choose two.)

A.

Interface poll time

B.

Peer hold time

C.

Interface failure limit

D.

Peer poll time

E.

Interface hold time

Question # 71

An administrator is attempting to add a Cisco Secure Firewall Threat Defence device to Cisco Secure Firewall Management Center with a password of Cisco0480846211 480846211. The private IP address of the FMC server is 192.168.75.201. Which command must be used in order to accomplish this task?

A.

configure manager add 192.168.75.201/24 < reg_key >

B.

configure manager add 192.16875.201 < reg_key >

C.

configure manager add 192.168.45.45 < reg_key > < nal-ld >

D.

configure manager add 192.168.75.201 255.255.255.0 < reg_key >

Question # 72

A network engineer must configure IPS mode on a Cisco Secure firewall Threat Defense device to inspect traffic and act as an IDS. The engineer already configured the passive-interface on the secure firewall threat Defence device and SPAN on the switch. What must be configured next by the engineer?

A.

intrusion policy on the Secure Firewall Threat Defense device

B.

active Interface on me Secure Firewall threat Defense device

C.

DHCP on the switch

D.

active SPAN port on the switch

Question # 73

What is a feature of Cisco AMP private cloud?

A.

It supports anonymized retrieval of threat intelligence

B.

It supports security intelligence filtering.

C.

It disables direct connections to the public cloud.

D.

It performs dynamic analysis

Question # 74

An administrator is attempting to add a new FTD device to their FMC behind a NAT device with a NAT ID of NAT001 and a password of Cisco0420l06525. The private IP address of the FMC server is 192.168.45.45. which is being translated to the public IP address of 209.165.200.225/27. Which command set must be used in order to accomplish this task?

A.

configure manager add 209.165.200.225 < reg_key > < nat_id >

B.

configure manager add 192.168.45,45 < reg_key > < nat_id >

C.

configure manager add 209.165.200.225 255.255.255.224 < reg_key > < nat_id >

D.

configure manager add 209.165.200.225/27 < reg_key > < nat_id >

Question # 75

Which two routing options are valid with Cisco Firepower Threat Defense? (Choose two.)

A.

BGPv6

B.

ECMP with up to three equal cost paths across multiple interfaces

C.

ECMP with up to three equal cost paths across a single interface

D.

BGPv4 in transparent firewall mode

E.

BGPv4 with nonstop forwarding

Question # 76

An engineer must implement Cisco Secure Firewall transparent mode due to a new server recently being added that must communicate with an existing server that is currently separated by the firewall. Which implementation action must be taken next by the engineer to accomplish the goal?

A.

Enable both servers to share the same VXLAN segment.

B.

Configure the same default gateway for both servers.

C.

Ensure that both servers are in the same bridge domain.

D.

Assign the same subnet to both servers.

Question # 77

A network administrator notices that inspection has been interrupted on all non-managed interfaces of a device. What is the cause of this?

A.

The value of the highest MTU assigned to any non-management interface was changed.

B.

The value of the highest MSS assigned to any non-management interface was changed.

C.

A passive interface was associated with a security zone.

D.

Multiple inline interface pairs were added to the same inline interface.

Question # 78

Which command is run on an FTD unit to associate the unit to an FMC manager that is at IP address 10.0.0.10, and that has the registration key Cisco123?

A.

configure manager local 10.0.0.10 Cisco123

B.

configure manager add Cisco123 10.0.0.10

C.

configure manager local Cisco123 10.0.0.10

D.

configure manager add 10.0.0.10 Cisco123

Question # 79

A network engineer detects a connectivity issue between Cisco Secure Firewall Management Center and Cisco Secure Firewall Threat Defense. Initial troubleshooting indicates that heartbeats and events are not being received. The engineer re-establishes the secure channels between both peers. Which two commands must the engineer run to resolve the issue? (Choose two.)

A.

show disk-manager

B.

show history

C.

sudo stats_unified.pl

D.

manage_procs.pl

E.

sudo perfstats -Cq < /var/sf/rna/correlator-stats/now

Question # 80

An engineer is attempting to create a new dashboard within the Cisco FMC to have a single view with widgets from many of the other dashboards. The goal is to have a mixture of threat and security related widgets along with Cisco Firepower device health information. Which two widgets must be configured to provide this information? (Choose two).

A.

Intrusion Events

B.

Correlation Information

C.

Appliance Status

D.

Current Sessions

E.

Network Compliance

Question # 81

An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration takes must be performed to achieve this file lookup? (Choose two.)

A.

The Cisco FMC needs to include a SSL decryption policy.

B.

The Cisco FMC needs to connect to the Cisco AMP for Endpoints service.

C.

The Cisco FMC needs to connect to the Cisco ThreatGrid service directly for sandboxing.

D.

The Cisco FMC needs to connect with the FireAMP Cloud.

E.

The Cisco FMC needs to include a file inspection policy for malware lookup.

Question # 82

There is an increased amount of traffic on the network and for compliance reasons, management needs visibility into the encrypted traffic What is a result of enabling TLS ' SSL decryption to allow this visibility?
A.

It prompts the need for a corporate managed certificate

B.

It has minimal performance impact

C.

It is not subject to any Privacy regulations

D.

It will fail if certificate pinning is not enforced

Question # 83

300-710 question answer

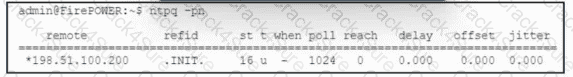
Refer to the exhibit. A security engineer views the health alerts in Cisco Secure Firewall Management Center by using the Health Monitor in the web interface. One of the alerts shows an appliance as critical because the Time Synchronization module status is out of sync. To troubleshoot the issue, the engineer runs the ntpq command in Secure Firewall Management Center. The output is shown in the exhibit. Which action must the security engineer take next to resolve the issue?

A.

Reset the appliance with a hard reboot.

B.

Reestablish the connection to the timeserver.

C.

Configure the appliance to receive the time from an NTP server.

D.

Configure the appliance to sync with its own internal clock.

Question # 84

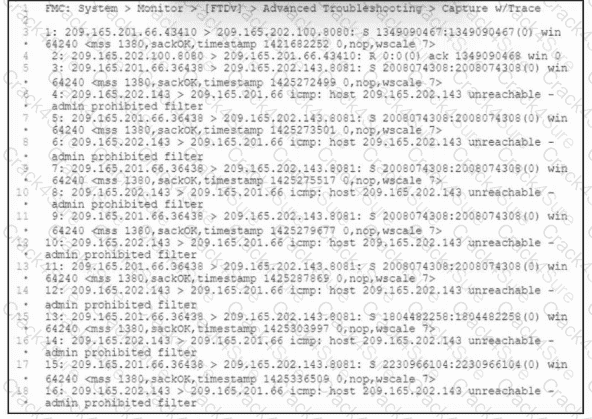
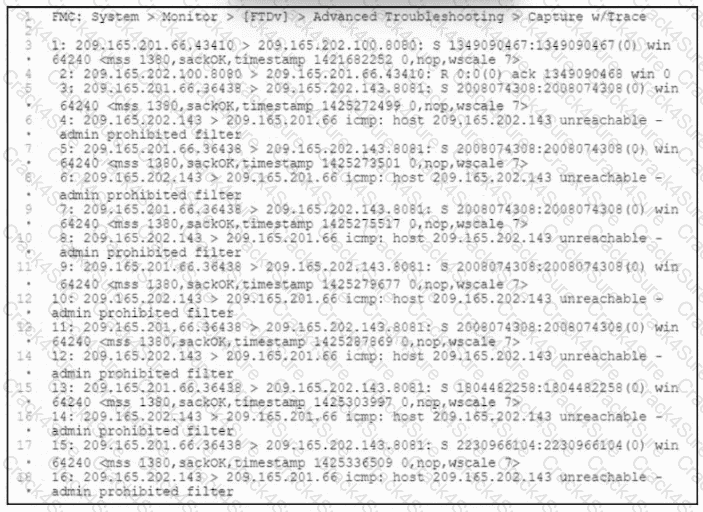
An engineer must investigate a connectivity issue from an endpoint behind a Cisco FTD device and a public DNS server. The endpoint cannot perform name resolution queries. Which action must the engineer perform to troubleshoot the issue by simulating real DNS traffic on the Cisco FTD while verifying the Snarl verdict?

A.

Perform a Snort engine capture using tcpdump from the FTD CLI.

B.

Use the Capture w/Trace wizard in Cisco FMC.

C.

Create a Custom Workflow in Cisco FMC.

D.

Run me system support firewall-engine-debug command from me FTD CLI.

Question # 85

An engineer configures an access control rule that deploys file policy configurations to security zones or tunnel zones, and it causes the device to restart. What is the reason for the restart?

A.

Source or destination security zones in the access control rule matches the security zones that are associated with interfaces on the target devices.

B.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the destination policy.

C.

Source or destination security zones in the source tunnel zone do not match the security zones that are associated with interfaces on the target devices.

D.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the source policy.

Question # 86

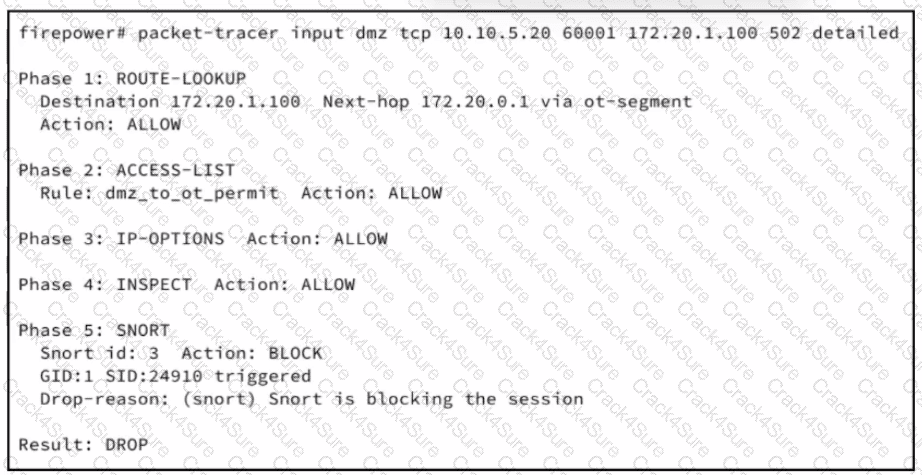
Refer to the exhibit.

300-710 question answer

At a manufacturing facility, a historian server 10.10.5.20 in the OT DMZ is intermittently unable to reach a remote PLC at 172.20.1.100 on TCP 502 Modbus. A security engineer runs packet-tracer on Cisco Secure Firewall Threat Defence and captures the output. The access policy is verified as correct. Which action must be performed to resolve the issue?

A.

Increase the MTU on the of-segment interface to prevent Modbus payload fragmentation during deep packet inspection.

B.

Disable logging for the rule matching traffic from 10.10.5.20 to 172.20.1.100 on port TCP 502 Modbus.

C.

Associate the ACP rule " dmz_to_of_permit " with a separate intrusion policy that excludes Modbus protocol signatures.

D.

Create intrusion policy exception for SID 24910 scoped to the historian-to-PLC Modbus flow with rule action to Alert/Generate Events.

Question # 87

A network administrator wants to configure a new Secure Firewall Threat Defense instance, which is managed by Cisco Secure Firewall Management Center, to load balance internet-bound traffic across multiple zones. Secure Firewall is connected to upstream ISP devices in multiple Zones. Which action must be taken to meet the requirement?

A.

Configure multiple static default routes to multiple zones towards upstream ISP devices.

B.

Enable BGP and OSPF towards upstream ISP devices.

C.

Implement OSPF and static route towards to upstream ISP devices.

D.

Add multiple dynamic routes set up via flex configuration to multiple zones.

Question # 88

An engineer defines a new rule while configuring an Access Control Policy. After deploying the policy, the rule is not working as expected and the hit counters associated with the rule are showing zero. What is causing this error?

A.

Logging is not enabled for the rule.

B.

The rule was not enabled after being created.

C.

The wrong source interface for Snort was selected in the rule.

D.

An incorrect application signature was used in the rule.

Question # 89

A network administrator is configuring Snort inspection policies and is seeing failed deployment messages in Cisco FMC. What information should the administrator generate for Cisco TAC to help troubleshoot?
A.

A " show tech " file for the device in question.

B.

A " troubleshoot " file for the device in question.

C.

A " troubleshoot " file for the Cisco FMC.

D.

A " show tech " for the Cisco FMC.

Question # 90

300-710 question answer

Refer to the exhibit. Users attempt to connect to numerous external resources on various TCP ports. If the users mistype the port, their connection closes immediately, and it takes more than one minute before the connection is torn down. An engineer manages to capture both types of connections as shown in the exhibit. What must the engineer configure to lower the timeout values for the second group of connections and resolve the user issues?

A.

Outbound access rule with the Block with reset action

B.

Outbound access rule that allows the entire ICMP protocol suite

C.

Inbound access rule that allows TCP reset packets from outside

Question # 91

A user within an organization opened a malicious file on a workstation which in turn caused a ransomware attack on the network. What should be configured within the Cisco FMC to ensure the file is tested for viruses on a sandbox system?

A.

Capacity handling

B.

Local malware analysis

C.

Spere analysis

D.

Dynamic analysis

Question # 92

A network engineer is receiving reports of users randomly getting disconnected from their corporate applications which traverses the data center FTD appliance Network monitoring tools show that the FTD appliance utilization is peaking above 90% of total capacity. What must be done in order to further analyze this issue?

A.

Use the Packet Export feature to save data onto external drives

B.

Use the Packet Capture feature to collect real-time network traffic

C.

Use the Packet Tracer feature for traffic policy analysis

D.

Use the Packet Analysis feature for capturing network data

Question # 93

An engineer is configuring a cisco FTD appliance in IPS-only mode and needs to utilize fail-to-wire interfaces. Which interface mode should be used to meet these requirements?

A.

transparent

B.

routed

C.

passive

D.

inline set

Question # 94

A security engineer found a suspicious file from an employee email address and is trying to upload it for analysis, however the upload is failing. The last registration status is still active. What is the cause for this issue?

A.

Cisco AMP for Networks is unable to contact Cisco Threat Grid on premise.

B.

Cisco AMP for Networks is unable to contact Cisco Threat Grid Cloud.

C.

There is a host limit set.

D.

The user agent status is set to monitor.

Question # 95

While integrating Cisco Umbrella with Cisco Threat Response, a network security engineer wants to automatically push blocking of domains from the Cisco Threat Response interface to Cisco Umbrella. Which API meets this requirement?

A.

investigate

B.

reporting

C.

enforcement

D.

REST

Question # 96

A network administrator is implementing an active/passive high availability Cisco FTD pair.

When adding the high availability pair, the administrator cannot select the secondary peer.

What is the cause?

A.

The second Cisco FTD is not the same model as the primary Cisco FTD.

B.

An high availability license must be added to the Cisco FMC before adding the high availability pair.

C.

The failover link must be defined on each Cisco FTD before adding the high availability pair.

D.

Both Cisco FTD devices are not at the same software Version

Question # 97

A network administrator observes an attempted attack from a specific IP address in Cisco Secure Firewall Management Center. Which Cisco security tool can be used directly from the Secure Firewall Management Center web interface to obtain additional information about the IP address?

A.

Cisco Threat Response browser plugin

B.

Cisco Secure Network Analytics

C.

Cisco Identity Services Engine

D.

Cisco Secure Endpoint

Question # 98

A network engineer is tasked with minimising traffic interruption during peak traffic limes. When the SNORT inspection engine is overwhelmed, what must be configured to alleviate this issue?

A.

Enable IPS inline link state propagation

B.

Enable Pre-filter policies before the SNORT engine failure.

C.

Set a Trust ALL access control policy.

D.

Enable Automatic Application Bypass.

Question # 99

Which command must be run to generate troubleshooting files on an FTD?

A.

system support view-files

B.

sudo sf_troubleshoot.pl

C.

system generate-troubleshoot all

D.

show tech-support

Question # 100

administrator is configuring SNORT inspection policies and is seeing failed deployment messages in Cisco FMC . What information should the administrator generate for Cisco TAC to help troubleshoot?

A.

A Troubleshoot " file for the device in question.

B.

A " show tech " file for the device in question

C.

A " show tech " for the Cisco FMC.

D.

A " troubleshoot " file for the Cisco FMC

Question # 101

Which policy rule is included in the deployment of a local DMZ during the initial deployment of a Cisco NGFW through the Cisco FMC GUI?

A.

a default DMZ policy for which only a user can change the IP addresses.

B.

deny ip any

C.

no policy rule is included

D.

permit ip any

Question # 102

A network engineer is extending a user segment through an FTD device for traffic inspection without creating another IP subnet How is this accomplished on an FTD device in routed mode?

A.

by leveraging the ARP to direct traffic through the firewall

B.

by assigning an inline set interface

C.

by using a BVI and create a BVI IP address in the same subnet as the user segment

D.

by bypassing protocol inspection by leveraging pre-filter rules

Question # 103

An engineer is deploying a Cisco Secure Firewall Management Center appliance. The company must send data to Cisco Secure Network Analytics appliances. Which two actions must the engineer take? (Choose two.)

A.

Configure Security Intelligence object to send data to Cisco Secure Network Analytics.

B.

Add the Netflow_Send_Destination object to the configuration.

C.

Add the Netflow_Add_Destination object to the configuration.

D.

Add the Netflow_Set_Parameters object to the configuration.

E.

Create a service identifier to enable the NetFlow service.

Question # 104

Refer to the exhibit.

300-710 question answer

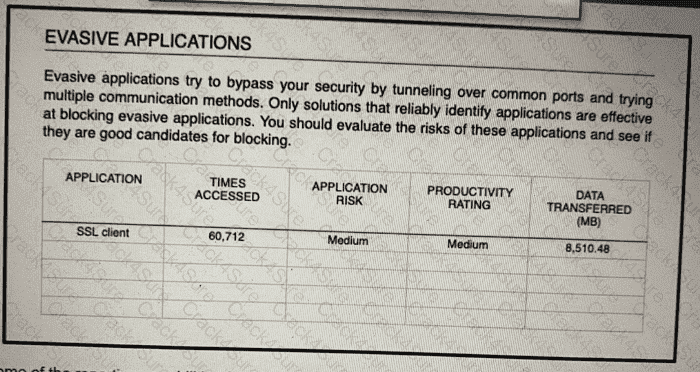
An administrator is looking at some of the reporting capabilities for Cisco Firepower and noticed this section of the Network Risk report showing a lot of SSL activity that cloud be used for evasion. Which action will mitigate this risk?

A.

Use SSL decryption to analyze the packets.

B.

Use encrypted traffic analytics to detect attacks

C.

Use Cisco AMP for Endpoints to block all SSL connection

D.

Use Cisco Tetration to track SSL connections to servers.

Question # 105

Refer to the exhibit.

300-710 question answer

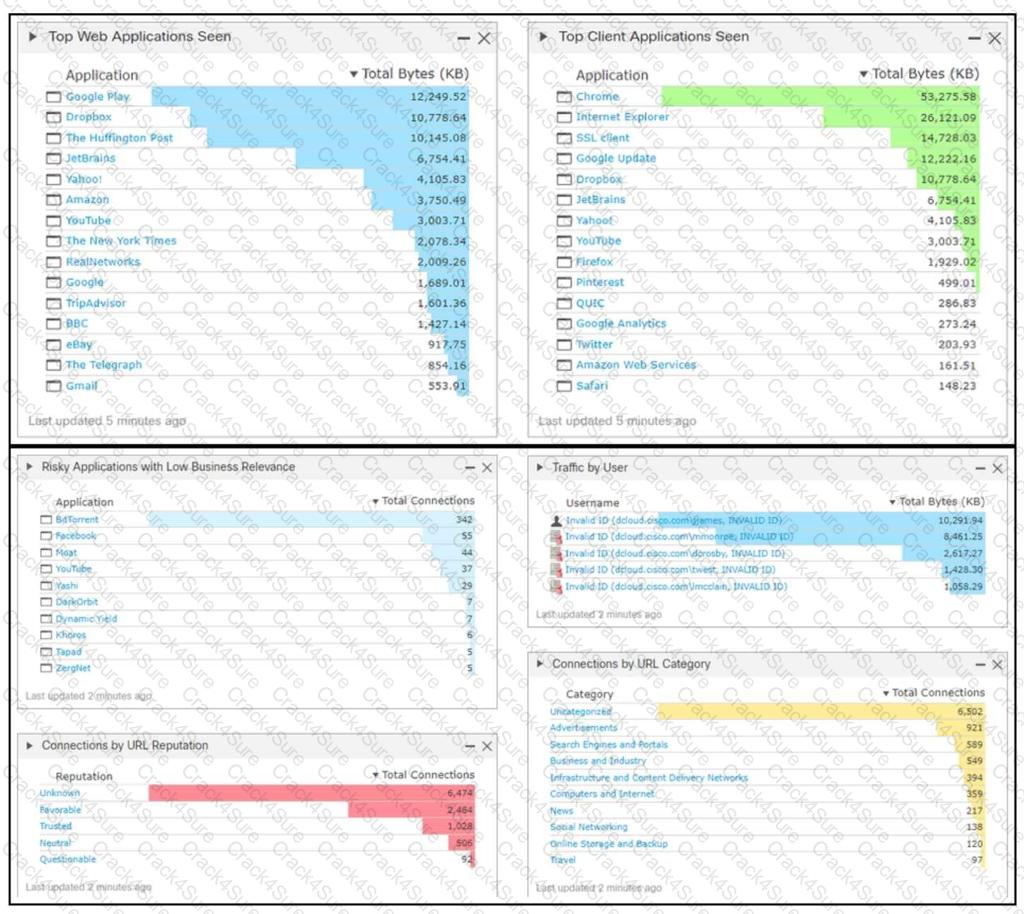
An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must the engineer take to decrease the application usage risk?

A.

Disable the use of Google Play.

B.

Disable the user account.

C.

Block all the BitTorrent applications.

D.

Patch all the Google Chrome browsers.

Question # 106

A network administrator is reviewing a monthly advanced malware risk report and notices a host that Is listed as CnC Connected. Where must the administrator look within Cisco FMC to further determine if this host is infected with malware?
A.

Analysis > Hosts > indications of Compromise

B.

Analysts > Files > Malware Events

C.

Analysis > Hosts > Host Attributes

D.

Analysis > Flies > Network File Trajectory

Question # 107

300-710 question answer

Refer to the exhibit. Users attempt to connect to numerous external resources on various TCP ports. If the users mistype the port, their connection closes immediately, and it takes more than one minute before the connection is torn down. An engineer manages to capture both types of connections as shown in the exhibit. What must the engineer configure to lower the timeout values for the second group of connections and resolve the user issues?

A.

outbound access rule that allows the entire ICMP protocol suite

B.

inbound access rule that allows ICMP Type 3 from outside

C.

inbound access rule that allows TCP reset packets from outside

D.

outbound access rule with the Block with reset action

Question # 108

A network engineer implements a new Cisco Firepower device on the network to take advantage of its intrusion detection functionality. There is a requirement to analyze the traffic going across the device, alert on any malicious traffic, and appear as a bump in the wire How should this be implemented?

A.

Specify the BVl IP address as the default gateway for connected devices.

B.

Enable routing on the Cisco Firepower

C.

Add an IP address to the physical Cisco Firepower interfaces.

D.

Configure a bridge group in transparent mode.

Question # 109

An engineer is configuring Cisco FMC and wants to allow multiple physical interfaces to be part of the same VLAN. The managed devices must be able to perform Layer 2 switching between interfaces, including sub-interfaces. What must be configured to meet these requirements?

A.

interface-based VLAN switching

B.

inter-chassis clustering VLAN

C.

integrated routing and bridging

D.

Cisco ISE Security Group Tag

Question # 110

A company is in the process of deploying intrusion protection with Cisco FTDs managed by a Cisco FMC. Which action must be selected to enable fewer rules detect only critical conditions and avoid false positives?

A.

Connectivity Over Security

B.

Balanced Security and Connectivity

C.

Maximum Detection

D.

No Rules Active

Question # 111

How should a high-availability pair of Cisco Secure Firewall Threat Defense Virtual appliances be deployed to Cisco Secure Firewall Management Center?

A.

Configure high availability first, then add only the primary Cisco Secure Firewall Threat Defense Virtual appliance to Cisco Secure Firewall Management Center.

B.

Add the primary and secondary Cisco Secure Firewall Threat Defense Virtual appliances to Cisco Secure Firewall Management Center first, then configure high availability.

C.

Add the primary appliance to Cisco Secure Firewall Management Center first, then configure high availability.

D.

Configure high availability first, then add the primary and secondary appliances to Cisco Secure Firewall Management Center.

Question # 112

An engineer integrates Cisco FMC and Cisco ISE using pxGrid. Which role is assigned for Cisco FMC?

A.

controller

B.

publisher

C.

client

D.

server

Question # 113

An engineer must configure a passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:

•Set the interface mode to Passive.

•Configure the MTU.

•Set the speed and duplex. Which action completes the configuration?

A.

Reset the NGIPS

B.

Reregister the NGIPS.

C.

Enable the bridge virtual interface.

D.

Enable the interface.

Question # 114

A security engineer is configuring an Access Control Policy for multiple branch locations. These locations share a common rule set and utilize a network object called INSIDE_NET which contains the locally significant internal network subnets at each location. Which technique will retain the policy consistency at each location but allow only the locally significant network subnet within the applicable rules?

A.

utilizing a dynamic Access Control Policy that updates from Cisco Talos

B.

utilizing policy inheritance

C.

creating a unique Access Control Policy per device

D.

creating an Access Control Policy with an INSIDE_NET network object and object overrides

Question # 115

A hospital network needs to upgrade their Cisco FMC managed devices and needs to ensure that a disaster recovery process is in place. What must be done in order to minimize downtime on the network?

A.

Configure a second circuit to an ISP for added redundancy

B.

Keep a copy of the current configuration to use as backup

C.

Configure the Cisco FMCs for failover

D.

Configure the Cisco FMC managed devices for clustering.

Question # 116

An engineer must implement static route tracking on a Cisco Secure Firewall Threat Defense appliance. Static route and IP SLA operation has already been configured. Static route must be removed from the routing table if the tracked object is unreachable. Which action must the engineer take next to meet the requirement?

A.

Implement a secondary route that has a higher precedence.

B.

Enable the IP SLA Responder on the backup path interface.

C.

Assign a tracking object to the static route and the IP SLA operation.

D.

Enable an ICMP redirect message on the interface connected to the backup path.

Question # 117

What must be implemented on Cisco Firepower to allow multiple logical devices on a single physical device to have access to external hosts?

A.

Add at least two container instances from the same module.

B.

Set up a cluster control link between all logical devices

C.

Add one shared management interface on all logical devices.

D.

Define VLAN subinterfaces for each logical device.

Question # 118

Which Firepower feature allows users to configure bridges in routed mode and enables devices to perform Layer 2 switching between interfaces?

A.

FlexConfig

B.

BDI

C.

SGT

D.

IRB

Question # 119

With Cisco FTD software, which interface mode must be configured to passively receive traffic that passes through the appliance?

A.

ERSPAN

B.

IPS-only

C.

firewall

D.

tap

Question # 120

An engineer wants to change an existing transparent Cisco FTD to routed mode.

The device controls traffic between two network segments. Which action is mandatory to allow hosts to reestablish communication between these two segments after the change?

A.

remove the existing dynamic routing protocol settings.

B.

configure multiple BVIs to route between segments.

C.

assign unique VLAN IDs to each firewall interface.

D.

implement non-overlapping IP subnets on each segment.

Question # 121

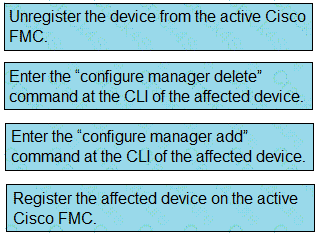
A network engineer is deploying a Cisco Firepower 4100 appliance and must configure a multi-instance environment for high availability. Drag and drop me actions from the left into sequence on the right far this configuration.
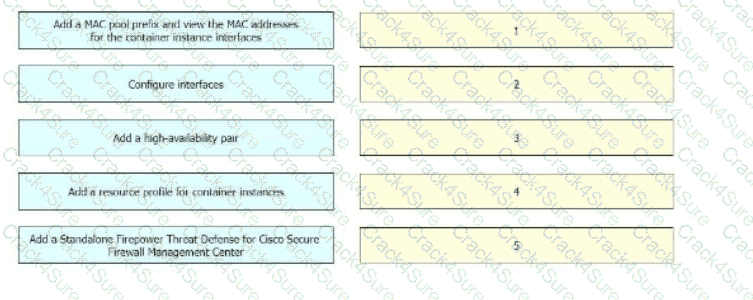
300-710 question answer

Question # 122

A network administrator is deploying a new Cisco Secure Firewall Threat Defense (FTD) firewall After Cisco Secure FTD is deployed, inside clients nave intermittent connectivity to each other. When … the packet capture on the Secure FTD firewall, the administrator sees that Secure FID is responding to all the AW requests on the inside network. Which action must the network administrator e to resolve the issue ' '

A.

Review NAT policy and disable incorrect proxy ARP configuration.

B.

Hardcode the MAC address of the FTD to IP mapping on client machines.

C.

Review the access policy and verify that ARP is allowed from inside to inside.

D.

Convert the FTD to transparent mode to allow ARP requests.

Question # 123

Cisco Security Analytics and Logging SaaS licenses come with how many days of data retention by default?

A.

60

B.

365

C.

90

D.

120

Question # 124

Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
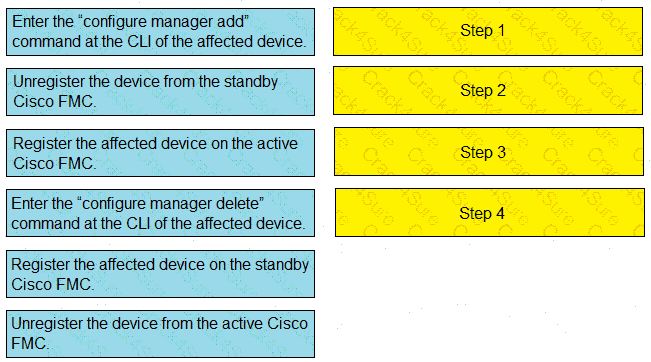
300-710 question answer

Question # 125

An engineer attempts to pull the configuration for a Cisco FTD sensor to review with Cisco TAC but does not have direct access to the CU for the device. The CLl for the device is managed by Cisco FMC to which the engineer has access. Which action in Cisco FMC grants access to the CLl for the device?

A.

Export the configuration using the Import/Export tool within Cisco FMC.

B.

Create a backup of the configuration within the Cisco FMC.

C.

Use the show run all command in the Cisco FTD CLI feature within Cisco FMC.

D.

Download the configuration file within the File Download section of Cisco FMC.

Question # 126

While configuring FTD, a network engineer wants to ensure that traffic passing through the appliance does not require routing or Vlan rewriting. Which interface mode should the engineer implement to accomplish this task?

A.

passive

B.

transparent

C.

Inline tap

D.

Inline set

Question # 127

Which CLI command is used to control special handling of ClientHello messages?

A.

system support ssl-client-hello-tuning

B.

system support ssl-client-hello-display

C.

system support ssl-client-hello-force-reset

D.

system support ssl-client-hello-enabled

Question # 128

Which connector is used to integrate Cisco ISE with Cisco FMC for Rapid Threat Containment?

A.

pxGrid

B.

FTD RTC

C.

FMC RTC

D.

ISEGrid

Question # 129

A network administrator registered a new FTD to an existing FMC. The administrator cannot place the FTD in transparent mode. Which action enables transparent mode?

A.

Add a Bridge Group Interface to the FTD before transparent mode is configured.

B.

Dereglster the FTD device from FMC and configure transparent mode via the CLI.

C.

Obtain an FTD model that supports transparent mode.

D.

Assign an IP address to two physical interfaces.

Question # 130

An organization created a custom application that is being flagged by Cisco Secure Endpoint. The application must be exempt from being flagged. What is the process to meet the requirement?

A.

Modify the custom detection list to exclude me custom application.

B.

Preculculate the hash value of the custom application and add it to the allowed applications.

C.

Configure the custom application to use the information-store paths.

D.

Add the custom application to the DFC 1st and update the policy.

Question # 131

A security engineer is adding three Cisco FTD devices to a Cisco FMC. Two of the devices have successfully registered to the Cisco FMC. The device that is unable to register is located behind a router that translates all outbound traffic to the router ' s WAN IP address. Which two steps are required for this device to register to the Cisco FMC? (Choose two.)

A.

Reconfigure the Cisco FMC lo use the device ' s private IP address instead of the WAN address.

B.

Configure a NAT ID on both the Cisco FMC and the device.

C.

Add the port number being used for PAT on the router to the device ' s IP address in the Cisco FMC.

D.

Reconfigure the Cisco FMC to use the device ' s hostname instead of IP address.

E.

Remove the IP address defined for the device in the Cisco FMC.

Question # 132

A network engineer detects a connectivity issue between Cisco Secure Firewall Management Centre and Cisco Secure Firewall Threat Defense Initial troubleshooting indicates that heartbeats and events not being received. The engineer re-establishes the secure channels between both peers Which two commands must the engineer run to resolve the issue? (Choose two.)

A.

manage_procs.pl

B.

sudo stats_unified.pl

C.

sudo perfstats -Cq < /var/sf/rna/correlator-stats/now

D.

show history

E.

show disk-manager

Question # 133

Which action should you take when Cisco Threat Response notifies you that AMP has identified a file as malware?

A.

Add the malicious file to the block list.

B.

Send a snapshot to Cisco for technical support.

C.

Forward the result of the investigation to an external threat-analysis engine.

D.

Wait for Cisco Threat Response to automatically block the malware.

300-710 PDF

$42

$139.99

3 Months Free Update

  • Printable Format
  • Value of Money
  • 100% Pass Assurance
  • Verified Answers
  • Researched by Industry Experts
  • Based on Real Exams Scenarios
  • 100% Real Questions

300-710 PDF + Testing Engine

$57

$189.99

3 Months Free Update

  • Exam Name: Securing Networks with Cisco Firepower (300-710 SNCF) v1.2
  • Last Update: Oct 8, 2026
  • Questions and Answers: 444
  • Free Real Questions Demo
  • Recommended by Industry Experts
  • Best Economical Package
  • Immediate Access

300-710 Engine

$48

$159.99

3 Months Free Update

  • Best Testing Engine
  • One Click installation
  • Recommended by Teachers
  • Easy to use
  • 3 Modes of Learning
  • State of Art Technology
  • 100% Real Questions included