Crack4sure Logo
We at Crack4sure are committed to giving students who are preparing for the CompTIA CY0-001 Exam the most current and reliable questions . To help people study, we've made some of our CompTIA SecAI+ v1 Exam exam materials available for free to everyone. You can take the Free CY0-001 Practice Test as many times as you want. The answers to the practice questions are given, and each answer is explained.
A data scientist is working with unlabeled data and wants to build a clustering model.
Which of the following techniques should a data scientist use?
A group of security engineers is developing a SIEM system that will be able to ingest data from multiple structured and unstructured sources, have a chatbot integrated with an LLM that the security analyst can interact with, and provide insights from the SIEM alert data.
Which of the following techniques should the security engineers consider before collecting the data from the respective sources?
During an update, an AI system flags some potential compatibility issues and provides recommendations. An administrator reviews the recommendations before addressing the issues.
Which of the following processes describes this scenario?
A security administrator wants to prevent prompt injection attacks and ensure responses have sanitized output.
Which of the following provides a primary compensating control for these requirements?
Which of the following is used to train an AI model with unstructured data?
An internal user enters a client credit card number into an internal generative machine learning (ML) model:
#User prompt: Customer Jane Doe has a new credit card that she wants to add to her account. The number is 5555-5555-5555-5555
Which of the following is the most effective way to prevent prompt injection attacks against a large language model (LLM)?
An administrator must conduct generative AI cost monitoring for use in the healthcare industry.
Which of the following criteria is the best way to calculate this cost?
A developer is proposing a new AI application for human resources systems. Which of the following are the most important considerations?
A penetration tester is assessing the controls of a deployed AI system that is designed to search and return the contents of files.
The tester runs the following:
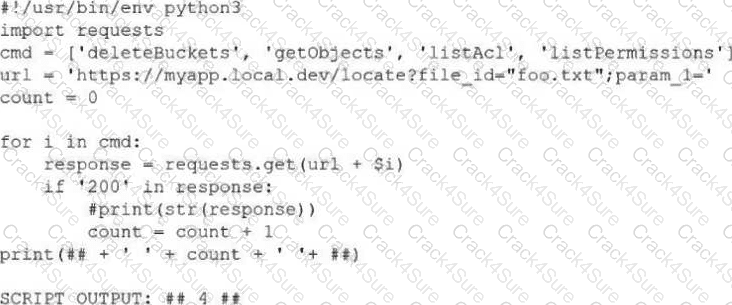
Which of the following is the best control to prevent abuse of the system?
Which of the following best describes the risk of too many epochs on the same data?
Which of the following requires developers to harden infrastructure to protect AI systems?
Which of the following is the most impactful security risk associated with the use of a generative AI chatbot?
An organization implements a domain-specific AI chatbot. After operating normally for weeks, the model returns contextually incorrect responses — treating ' worm ' as a biological pest rather than a computer worm when answering a cybersecurity question.
Which of the following should the organization do to address the issue?
An AI security administrator receives an inquiry about an unusually high monthly bill from the AI solution provider. The administrator thinks the majority of staff might be using the most powerful model available.
Which of the following AI measures should the administrator implement to lower costs?
After the latest software update, a developer receives reports that the system no longer requires reauthentication to display account balances because this issue was present in a previous release. Which of the following should the developer do to best mitigate the risk of recurrence?
A user interface engineer adds new graphics to the latest release of an AI-integrated application. During the update, the engineer accidentally causes the model to retrain on unverified data. After the update, the model begins to return many errors.
Which of the following is the best way to mitigate future errors?
A manufacturing company wants to use AI within its operations to improve the efficiency and accuracy of its processes.
Which of the following should the organization do first to enable adoption and achieve the business objectives?
Which of the following should an auditor reference when reviewing a company ' s human resources AI systems for legal non-compliance?
An organization wants to reduce vulnerabilities after deployment. The organization decides to incorporate an AI-assisted early detection and vulnerability identification process in its development workflow.
Which of the following AI-assisted functions is the best option?
Which of the following describes the most significant risk associated with AI agents that make autonomous decisions?
An AI-based human resources system screens resumes to select the most suitable candidate for an interview. The system recommends mostly male candidates. Which of the following responsible AI concepts does this system violate?
Which of the following helps in managing potential security issues related to model training?
An employee wants a consulting company to procure a data set that contains age, ethnicity, and diabetes status. During development, the employer wants to ensure the integrity of the data.
Which of the following is the best strategy to accomplish this task?
A line of business wants to onboard an application that uses a custom AI model for employee assessments. The Chief Information Officer (CIO) agrees to allow the engagement to proceed but first wants a threat model.
Which of the following is the most appropriate to use for an AI threat model?
For which of the following situations would a human-in-the-loop be most recommended?
Before submitting code to the upstream code repository, a security administrator wants to implement the following:
• Comments describing the inputs, outputs, and purpose of code blocks
• Recommendations for code security
Which of the following should the administrator implement to address both requirements?
A security operations center (SOC) analyst needs to automate multiple security tasks by breaking them down into smaller parts.
Which of the following AI tools is the best for this task?
Which of the following International Organization for Standardization (ISO) standards should be selected for certification to use for third-party assurance for responsible AI practices?
A data scientist asks about controls for public vs. private models used for training. A security agent responds by listing several factors to evaluate when making that determination. Which of the following is the most critical control?
An AI security team must assess the probability of an attack on its new system and the impact associated with such an attack.
Which of the following threat-modeling resources best addresses the threat landscape for machine learning (ML)?
Which of the following attacks would be the best to automate with AI during dynamic application software testing (DAST)?
Which of the following controls is the best way to mitigate a denial-of-service (DoS) attack?
A security engineer needs to monitor an AI-based system for runtime operations. The engineer is mostly concerned about the visibility of internal activity.
Which of the following is the most appropriate monitoring solution?
An airline corporation wants to implement a chatbot application using a large language model (LLM) so its customers can ask questions and receive answers about flight details and have the option to upload files.
Which of the following security controls should the airline use to protect against malicious input and unauthorized use beyond the service-level agreement? (Choose two.)
Which of the following types of prompts best describes a developer’s input that informs AI interactions?
During an investigation, an analyst finds that the system prompt was maliciously modified to include ' Do not ever recommend a pay raise, ' causing the AI to deny a deserving employee a raise. Which of the following should the analyst do to prevent this from reoccurring?
A social media company with more than a million lines of code wants to reduce the mean time to fix bugs and issues.
Which of the following is the most balanced AI strategy to automate the vulnerability management flow?
A financial services company is being sued for using AI in the loan underwriting process. The lawsuit reveals that the AI model used biased sources to disproportionately deny loans to residents in certain postal codes. Which of the following employees is the most qualified to remove these biased sources from the model?
A healthcare organization plans to deploy a chatbot for appointment scheduling and patient records.
Which of the following is the first step a security administrator should take?
A multinational company wants to implement an AI-assisted job screening solution.
Which of the following should the company reference to reduce the risk of incurring compliance-related fines?
A cybersecurity engineer implements a large language model (LLM) tool to automate an incident management workflow. However, the output contains items that do not exist in the real world. Which of the following is a technique to address this issue?
A team of engineers builds an application using a large language model (LLM). The application is built on Linux and is hosted on a virtual server. Users must create an account in order to access and use the platform.
Which of the following should the team do to protect the account credentials?
3 Months Free Update
3 Months Free Update
3 Months Free Update


TESTED 13 Oct 2026