Black Friday Flash Blitz - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75special

Practice Free GUARD CyberArk Guardian Exam Exam Questions Answers With Explanation

We at Crack4sure are committed to giving students who are preparing for the CyberArk GUARD Exam the most current and reliable questions . To help people study, we've made some of our CyberArk Guardian Exam exam materials available for free to everyone. You can take the Free GUARD Practice Test as many times as you want. The answers to the practice questions are given, and each answer is explained.

Question # 6

A customer has a hybrid infrastructure that spans multiple cloud vendors and privately owned data centers. They deployed CyberArk PAM in AWS by using CyberArk-provided scripts. Eighty percent of the customer’s infrastructure is located in privately owned data centers. The customer is concerned about availability between the cloud provider and the data center. They are cloud-first and are gradually migrating their servers to the cloud.

Active Master Policy settings:

• Require dual-control approval for password access

• Enforce exclusive check-in/check-out access

• Require password changes every 25 days

• Require password verification every 7 days

What is the most appropriate recommendation for the customer?

A.

Keep the deployment as is in AWS.

B.

Deploy an active CPM to the privately owned Data Center.

C.

Deploy a separate infrastructure in another cloud vendor.

D.

Migrate the CPM to the privately owned Data Center.

Question # 7

A customer has asked you to onboard more than 1,000 Local Admin accounts. All of the accounts are used by the same team and are in a control zone.

Which CyberArk feature provides an automated way to accomplish this task?

A.

Password Upload Utility

B.

Auto-Detection

C.

Auto-Reconcile

D.

Remote Control Agent

Question # 8

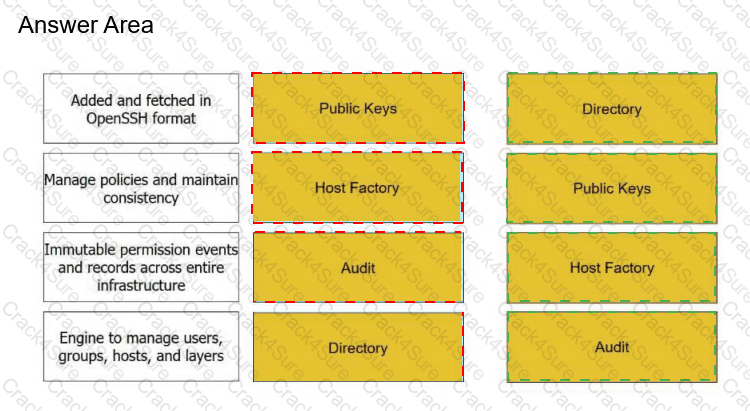
Match the Conjur services and options:
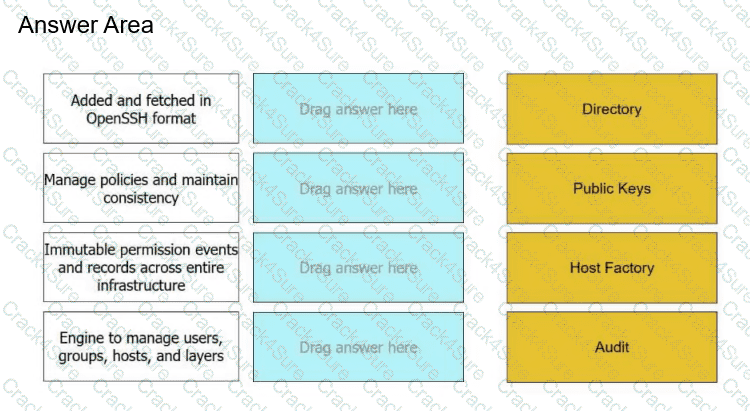
GUARD question answer

Question # 9

A financial institution uses CyberArk Privileged Session Manager (PSM) to monitor privileged access to production servers.

The security team requires authorized auditors to terminate suspicious privileged sessions immediately when potentially malicious administrative activity is detected.

An auditor can view active sessions in PVWA but cannot terminate them. The administrator confirms that session monitoring is enabled and the PSM infrastructure is functioning correctly.

What configuration should be implemented to allow the auditor to terminate active privileged sessions?

A.

Add the auditor to the Vault Administrators group and grant full administrative access to all Recording Safes.

B.

Enable the Require Dual Control Password Access Approval rule in the Master Policy and assign the auditor as an approver.

C.

Add the auditor to the PSMLiveSessionTerminators group and ensure that this group has the required membership in the Safes containing the managed accounts.

D.

Assign the auditor the Retrieve Accounts permission on the relevant Safes and enable automatic password reconciliation.

Question # 10

What encryption capability is required for the HSM?

A.

The HSM must support AES-192 encryption in ECB mode.

B.

The HSM must support Triple Data Encryption Standard (TripleDES).

C.

The HSM must support AES-256 encryption in ECB and CBC modes.

D.

The HSM must support Blowfish encryption algorithm.

Question # 11

You deployed your Primary Vault on a CyberArk-supported cloud platform by using a CyberArk-provided image, and deployed a DR Vault in a privately owned data center.

What is the best method for securing the Server Key on the DR Vault?

A.

Use KMS.

B.

Use HSM.

C.

Mount Operator CD every time Vault is started.

D.

Use Azure Key Vault.

Question # 12

How can a Secondary PTA server be promoted to a Primary PTA Server?

A.

A manual procedure.

B.

Automatically using the PTA Network Sensors.

C.

This is not possible.

D.

Automatically using a BASH script.

Question # 13

A new Vault is to be deployed in a highly regulated environment. Regulations require that every operating system on the network be updated regularly.

How does CyberArk recommend automatically updating hardened Vaults?

A.

Using a dedicated WSUS server and install patches monthly.

B.

Vaults do not require OS updates.

C.

Manually install updates whenever CyberArk notifies you.

D.

Integrate the Vault with the domain for monthly updates.

Question # 14

Communication is an integral component of any PAM program and includes these two elements.

Choose two

A.

Getting buy-in from leadership and communicating this from the first stakeholder meeting.

B.

Allowing each level to develop their own messaging so that we can build a specific message catered to each group's goals: leadership, management, different organizations, IT Administrators, etc..

C.

Developing a PAM sponsor to evangelize the project goals with the CTO and the entire technology organization.

D.

"One and Done" communication so we don't overwhelm users.

E.

Developing all training materials in Stage 2 of the program so that we can include 'lessons learned'.

Question # 15

At which stage is it appropriate to incorporate the C3 Alliance integrations?

A.

Since we already have integrations available and little development is required, they should all be completed in Stage 1.

B.

Integrate the security tools in Stage 1 and other tools such as RPA in Stage 2.

C.

They are less of a risk, so we should leave them until Stage 3 and focus on other privileged accounts first.

D.

They should all be integrated prior to the actual ’go-live' of CyberArk PAM.

Question # 16

What should be the focus of Stage 1 of the CyberArk Blueprint?

A.

Primarily identities, accounts and systems that have the ability to control an entire environment, both in the cloud or on-prem.

B.

Universal technology platforms such as *NIX and Windows local accounts.

C.

High Risk/High Reward value use cases that are most critical to the operation of the business.

D.

Building integrations to CyberArk PAM such as automation, onboarding and dual control workflows.

Question # 17

Which option listed below is an advanced Master Policy rule?

A.

Allow users to select a reason for access.

B.

Allow Manual Change.

C.

Allow Users to View Passwords.

D.

Only Administrators can approve password access.

Question # 18

You need to implement a solution that requires users to verify they have run an application.

Which solution is best?

A.

EPM Step-up authentication.

B.

Accounts with Least Privilege configured.

C.

Ad Hoc Access and Ad Hoc Connections.

D.

PTA Risky Commands.

GUARD PDF

$27.5

$109.99

3 Months Free Update

  • Printable Format
  • Value of Money
  • 100% Pass Assurance
  • Verified Answers
  • Researched by Industry Experts
  • Based on Real Exams Scenarios
  • 100% Real Questions

GUARD PDF + Testing Engine

$44

$175.99

3 Months Free Update

  • Exam Name: CyberArk Guardian Exam
  • Last Update: Nov 22, 2026
  • Questions and Answers: 60
  • Free Real Questions Demo
  • Recommended by Industry Experts
  • Best Economical Package
  • Immediate Access

GUARD Engine

$33

$131.99

3 Months Free Update

  • Best Testing Engine
  • One Click installation
  • Recommended by Teachers
  • Easy to use
  • 3 Modes of Learning
  • State of Art Technology
  • 100% Real Questions included