Crack4sure Logo
We at Crack4sure are committed to giving students who are preparing for the Microsoft SC-100 Exam the most current and reliable questions . To help people study, we've made some of our Microsoft Cybersecurity Architect exam materials available for free to everyone. You can take the Free SC-100 Practice Test as many times as you want. The answers to the practice questions are given, and each answer is explained.
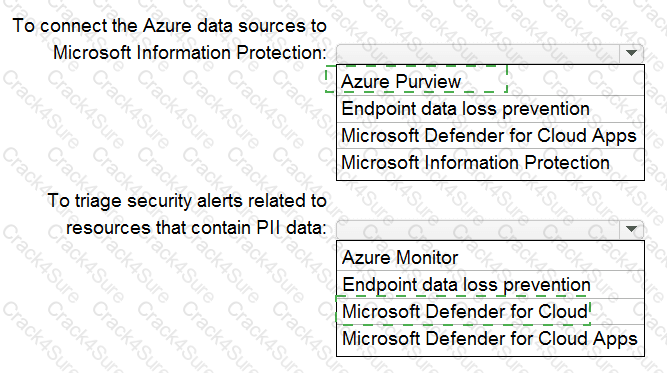
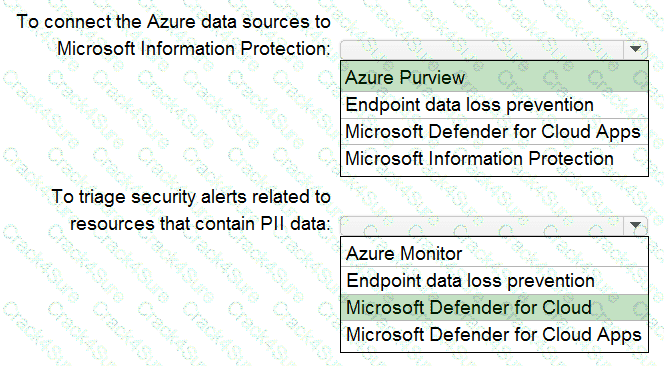
Your company is migrating data to Azure. The data contains Personally Identifiable Information (Pll). The company plans to use Microsoft Information Protection for the Pll data store in Azure. You need to recommend a solution to discover Pll data at risk in the Azure resources.
What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
To meet the application security requirements, which two authentication methods must the applications support? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
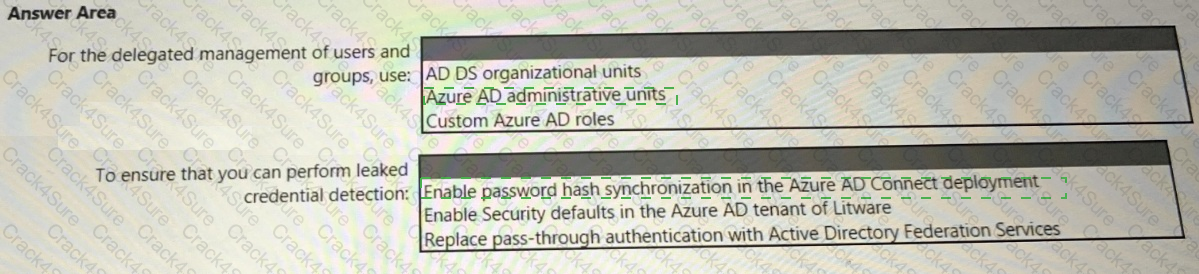
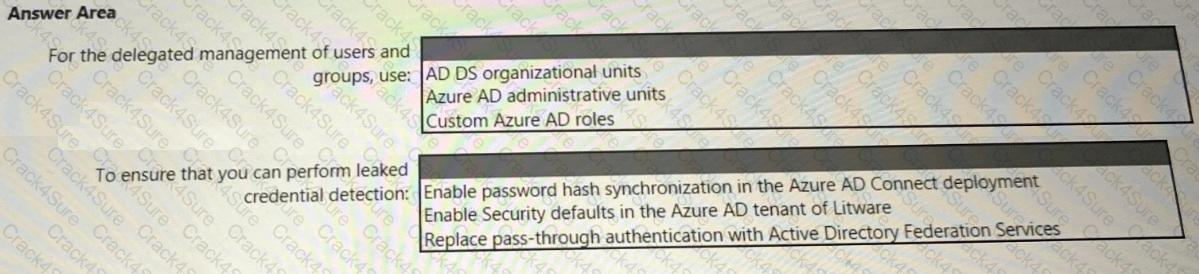
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
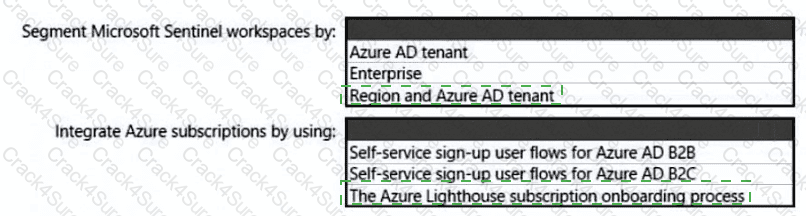
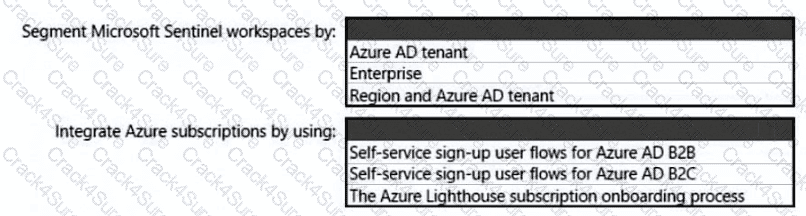
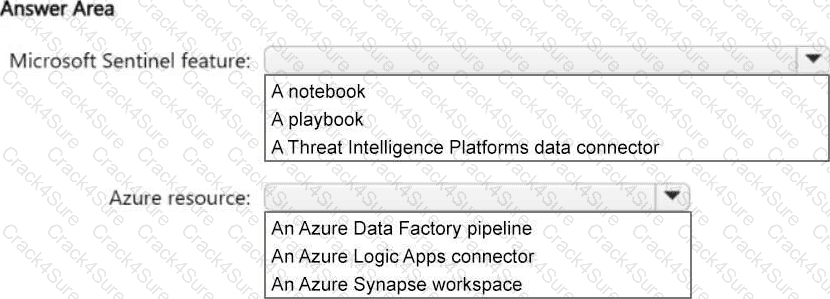
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
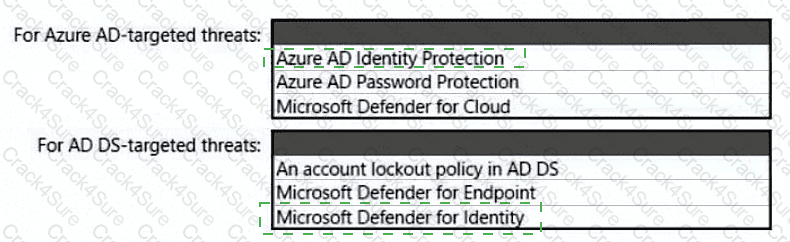
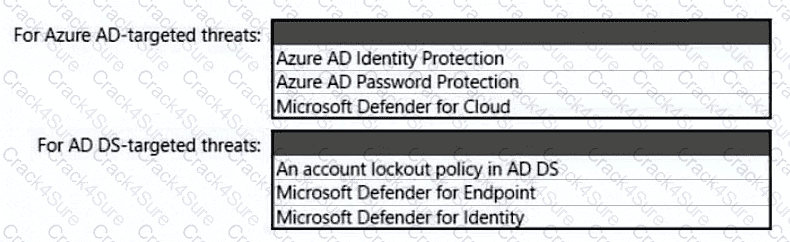
You need to recommend a strategy for securing the litware.com forest. The solution must meet the identity requirements. What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE; Each correct selection is worth one point.
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains 50 virtual machines. Each virtual machine runs different applications on Windows Server 2019.
You need to recommend a solution to ensure that only authorized applications can run on the virtual machines. If an unauthorized application attempts to run or be installed, the application must be blocked automatically until an administrator authorizes the application.
Which security control should you recommend?
You need to design a strategy for securing the SharePoint Online and Exchange Online data. The solution must meet the application security requirements.
Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.
Your company plans to evaluate the security of its Azure environment based on the principles of the Microsoft Cloud Adoption Framework for Azure.
You need to recommend a cloud-based service to evaluate whether the Azure resources comply with the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF).
What should you recommend?
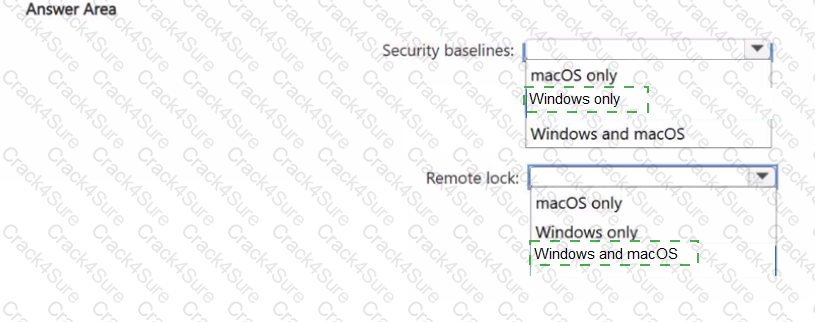
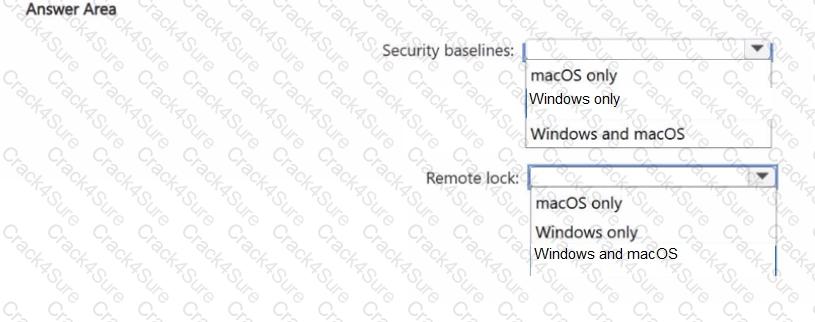
You have 500 Windows 11 devices and 200 macOS devices. The devices are managed by using Microsoft Intune and are subject to compliance policies.
You plan to deploy the following Intune features:
• Security baselines
• Remote lock of noncompliant devices
Which feature will be supported by each platform? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
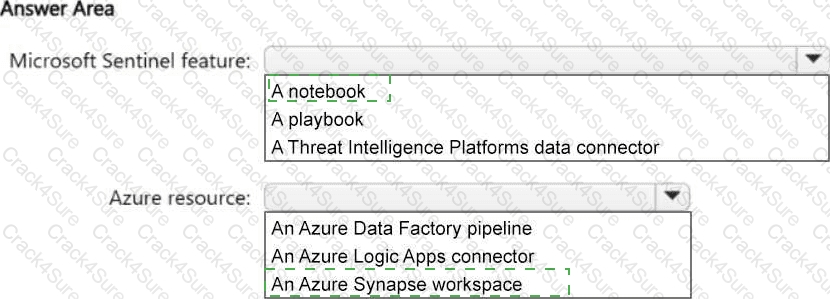
You have an Azure subscription that contains a Microsoft Sentinel workspace named MWS1 and an Azure Data Lake Storage account named lake1. Firewall log data is ingested into MWS1.
You plan to export historical firewall log data from MWS1 to lake1.
You need to ensure that security analysts can perform threat hunting from MWS1. The solution must ensure that the firewall logs stored in lake1 can be included in threat hunting queries.
What should you configure? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
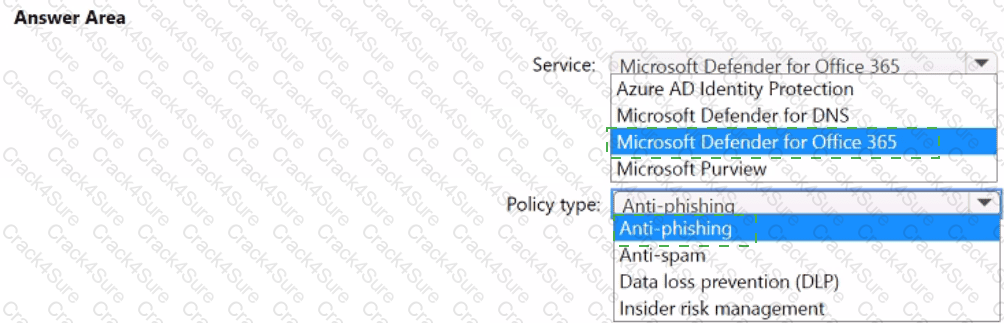
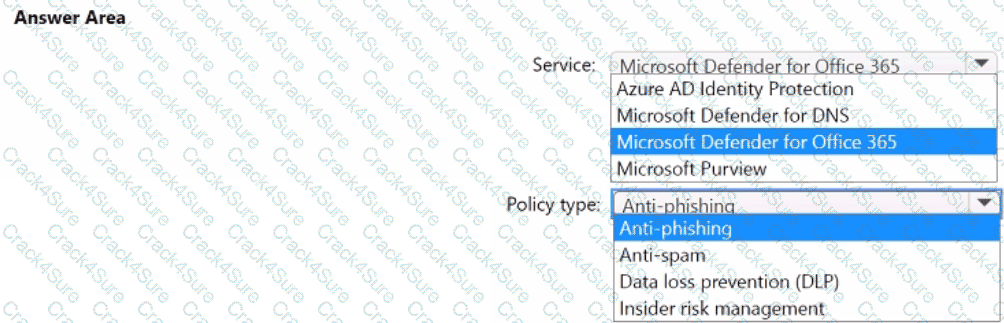
You have a Microsoft 365 E5 subscription that uses Microsoft Exchange Online.
You need to recommend a solution to prevent malicious actors from impersonating the email addresses of internal senders.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains SQL Server on Azure virtual machines located in the West US Azure region. The virtual machines are only accessible by using private IP addresses.
You plan to deploy a Windows-based Azure App Service web apps in the East US Azure region.
You need to recommend a solution to provide the web apps access to the SQL Server databases.
What should you include in the recommendation?
You plan to implement an Azure environment based on Microsoft Cloud Adoption Framework for enterprise-scale landing zone architecture principles .
The environment will host three apps that have the following characteristics:
• Each app will have a development environment, a test environment, and a production environment.
• Each environment will be managed by a separate team.
• Each app will store its secrets in Azure Key Vault.
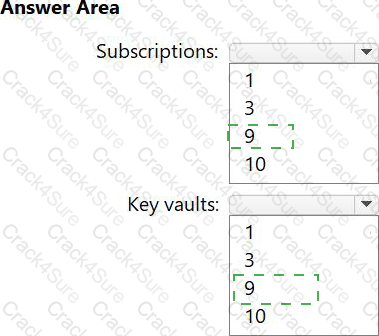
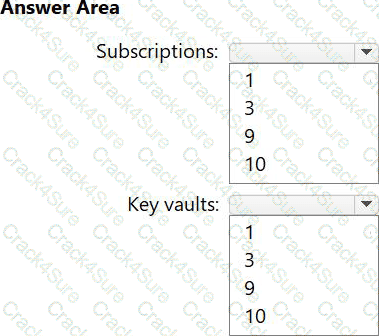
You need to recommend how many Azure subscriptions and key vaults to deploy to the application landing zones.
What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Your company has an office in Seattle.
The company has two Azure virtual machine scale sets hosted on different virtual networks.
The company plans to contract developers in India.
You need to recommend a solution provide the developers with the ability to connect to the virtual machines over SSL from the Azure portal. The solution must meet the following requirements:
• Prevent exposing the public IP addresses of the virtual machines.
• Provide the ability to connect without using a VPN.
• Minimize costs.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
You are designing the encryption standards for data at rest for an Azure resource
You need to provide recommendations to ensure that the data at rest is encrypted by using AES-256 keys. The solution must support rotating the encryption keys monthly.
Solution: For blob containers in Azure Storage, you recommend encryption that uses Microsoft-managed keys within an encryption scope.
Does this meet the goal?
You have an Azure subscription that contains Azure App Service web apps. The apps have the following characteristics:
• The apps are deployed by using continuous integration and continuous deployment (CI/CD) pipelines in Azure DevOps.
• The apps are deployed to a test environment first, and then to a production environment.
• The source code for the apps is stored in Azure Repos.
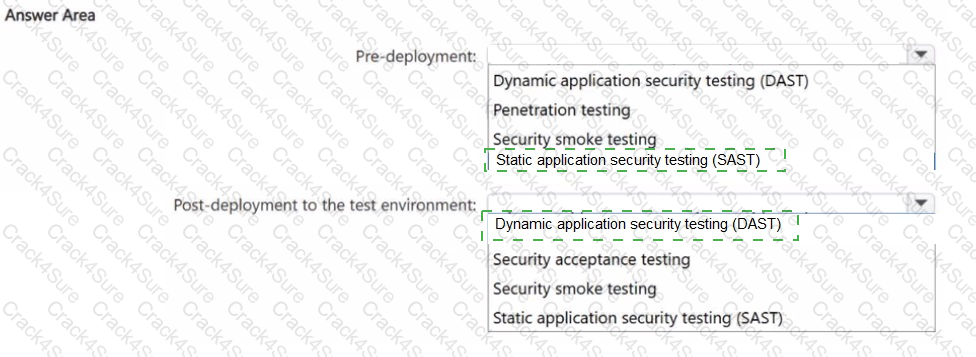
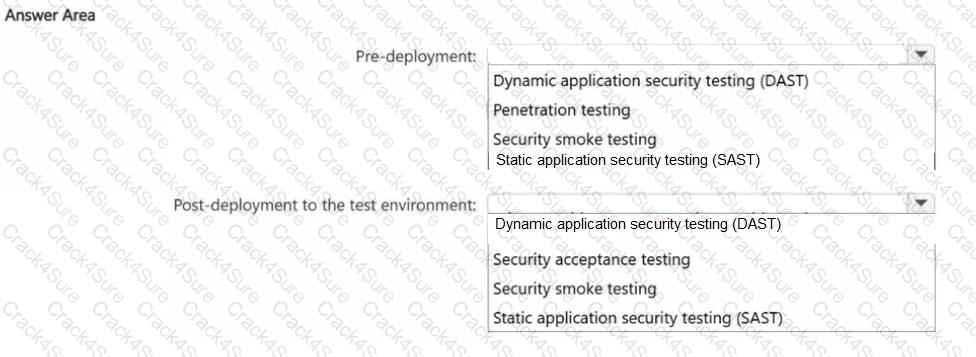
You plan to implement DevSecOps controls based on the Microsoft Cloud Adoption Framework for Azure. You need to recommend testing controls to meet the following requirements:
• All the source code must be tested for security vulnerabilities in Azure Repos before deploying the apps.
• Once the apps are deployed to the test environment they must be tested for security vulnerabilities.
Which testing method should you recommend for each stage? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
You are designing a security operations strategy based on the Zero Trust framework.
You need to minimize the operational load on Tier 1 Microsoft Security Operations Center (SOC) analysts.
What should you do?
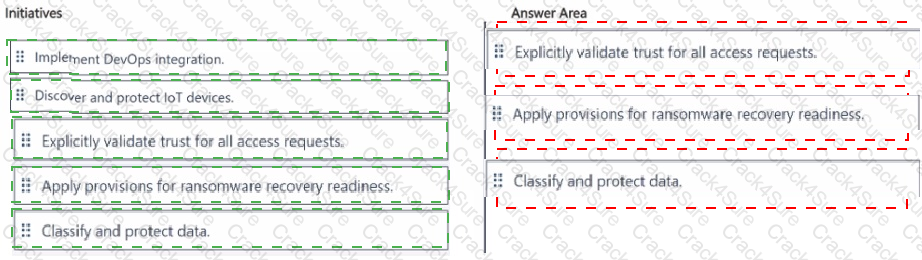
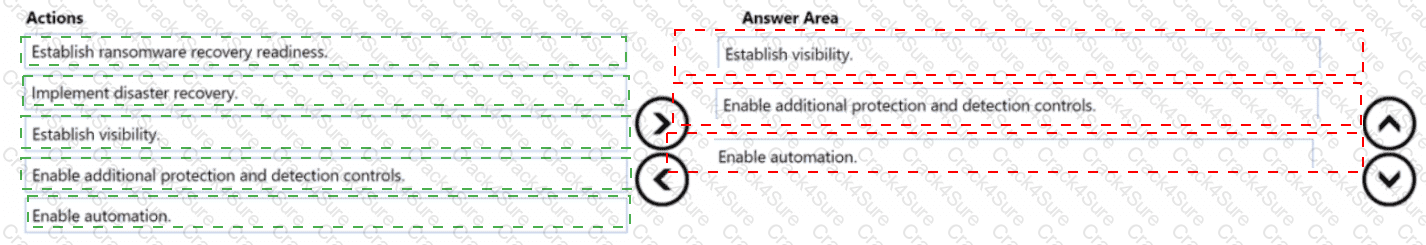
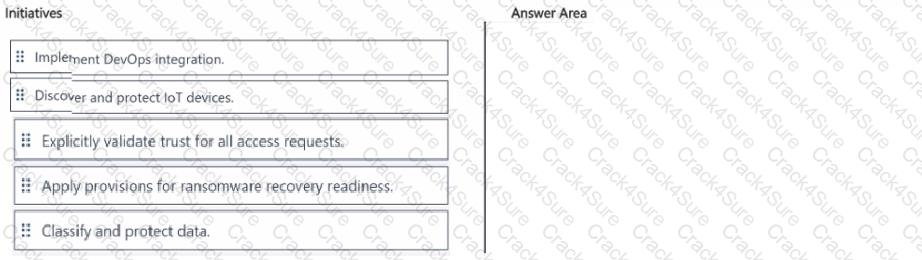
You need to design a solution to accelerate a Zero Trust security implementation. The solution must be based on the Zero Trust Rapid Modernization Plan (RaMP).
Which three initiatives should you include in the solution, and in which order should you implement the initiatives? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription.
You have a Conditional Access policy that has the following settings:
• Name: Policy 1
• Assignments o Users:
- Include: All users o Target resources
- Include: Select apps; Office 365 o Network
- Include: Any network or location
- Exclude: Selected networks and locations; Site1 o Access controls
- Grant: Require multifactor authentication, Require Hybrid Microsoft Entra joined device
You plan to implement Zero Trust Rapid Modernization Plan (RaMP).
You need to ensure that Policy1 aligns with best practice recommendations in RaMP.
Which setting should you change?
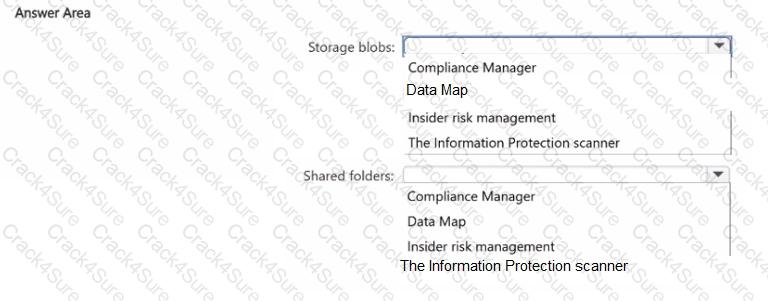
You have three on-premises servers that run Windows Server and contain shared folders. The folders contain 10,000 files.
You have a Microsoft 365 tenant that uses Microsoft Purview and includes custom sensitive information types (SITs).
You have an Azure subscription that contains five Azure Blob Storage accounts and multiple App Service web apps. The Blob Storage accounts contain data for the web apps.
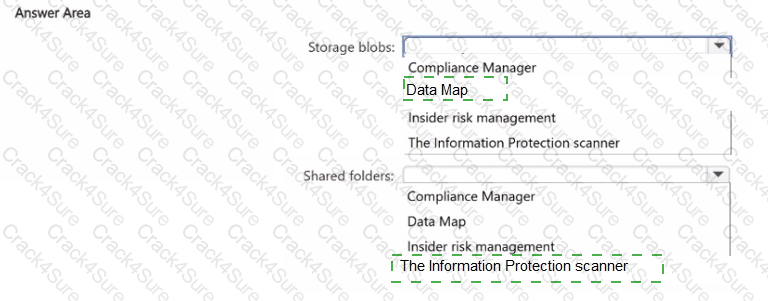
You need to recommend a Microsoft Purview solution to scan the storage blobs and the shared folders. The solution must use the custom SITs to identify files that contain specific data.
What should you use for each type of storage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk
• Blocks user access to Saas apps that Microsoft has identified as high risk
Solution: From the Microsoft Defender portal, you set Web content filtering to On and create a web content filtering policy. Does this meet the goal?
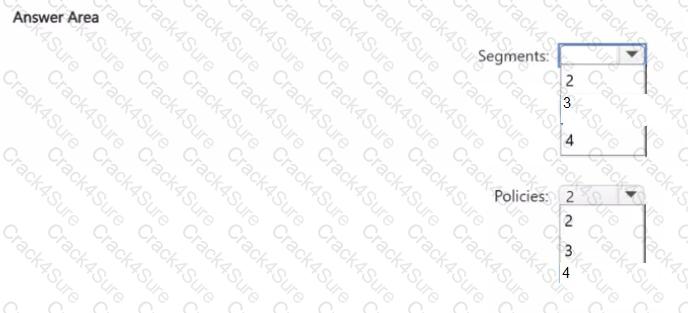
You have a Microsoft 365 E5 subscription that uses Microsoft Teams.
Your company has an investment department and a research department Each department has a compliance team.
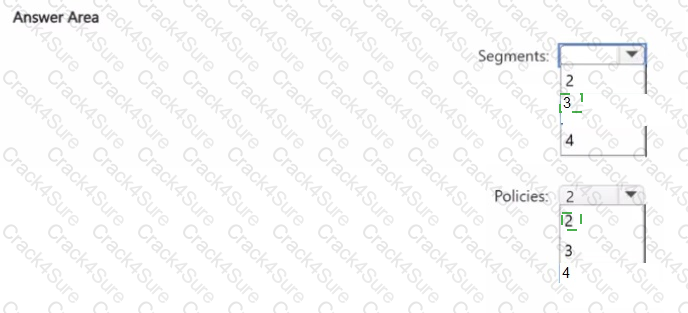
You are designing a Microsoft Purview Information Barriers (IBs) solution to restrict communication between the departments. The solution must meet the following requirements:
• The employees in each department must only be able to communicate with the employees in their respective department.
• The employees on the compliance team of each department must be able to communicate with the employees on the compliance team of the other department
What is the minimum number of segments and IB policies required? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company develops several applications that are accessed as custom enterprise applications in Azure Active Directory (Azure AD). You need to recommend a solution to prevent users on a specific list of countries from connecting to the applications. What should you include in the recommendation?
You have an Azure AD tenant that syncs with an Active Directory Domain Services {AD DS) domain. Client computers run Windows and are hybrid-joined to Azure AD.
You are designing a strategy to protect endpoints against ransomware. The strategy follows Microsoft Security Best Practices.
You plan to remove all the domain accounts from the Administrators group on the Windows computers.
You need to recommend a solution that will provide users with administrative access to the Windows computers only when access is required. The solution must minimize the lateral movement of ransomware attacks if an administrator account on a computer is compromised.
What should you include in the recommendation?
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points.
You need to recommend configurations to increase the score of the Secure management ports controls.
Solution: You recommend enabling just-in-time (JIT) VM access on all virtual machines.
Does this meet the goal?
You are designing the encryption standards for data at rest for an Azure resource
You need to provide recommendations to ensure that the data at rest is encrypted by using AES-256 keys. The solution must support rotating the encryption keys monthly.
Solution: For blob containers in Azure Storage, you recommend encryption that uses customer-managed keys (CMKs).
Does this meet the goal?
You are designing a ransomware response plan that follows Microsoft Security Best Practices-
You need to recommend a solution to limit the scope of damage of ransomware attacks without being locked out.
What should you include in the recommendations?
You are designing a security operations strategy based on the Zero Trust framework.
You need to increase the operational efficiency of the Microsoft Security Operations Center (SOC).
Based on the Zero Trust framework, which three deployment objectives should you prioritize in sequence? To answer, move the appropriate objectives from the list of objectives to the answer area and arrange them in the correct order.
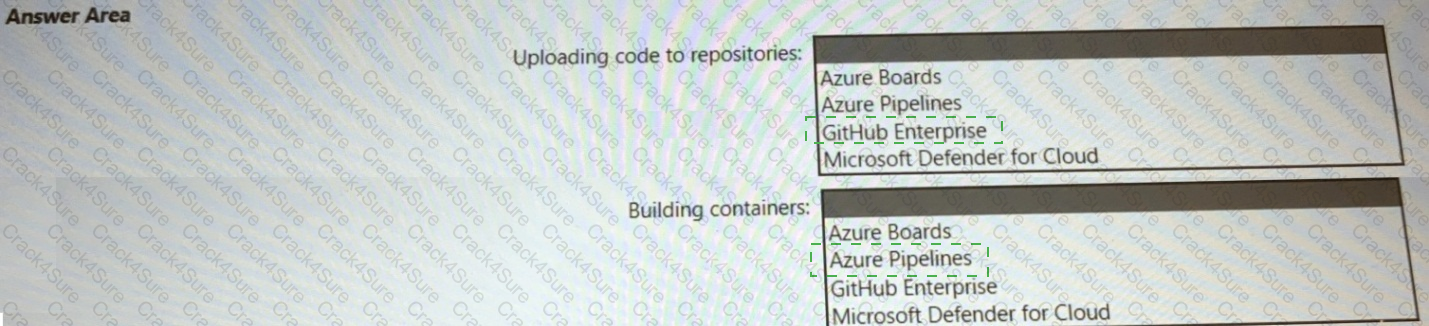
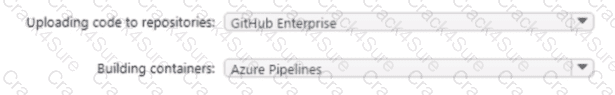
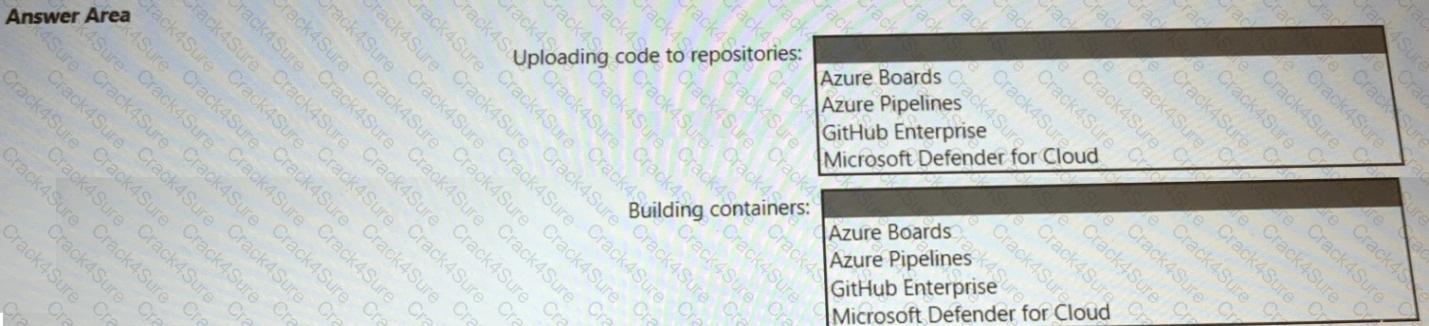
Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.
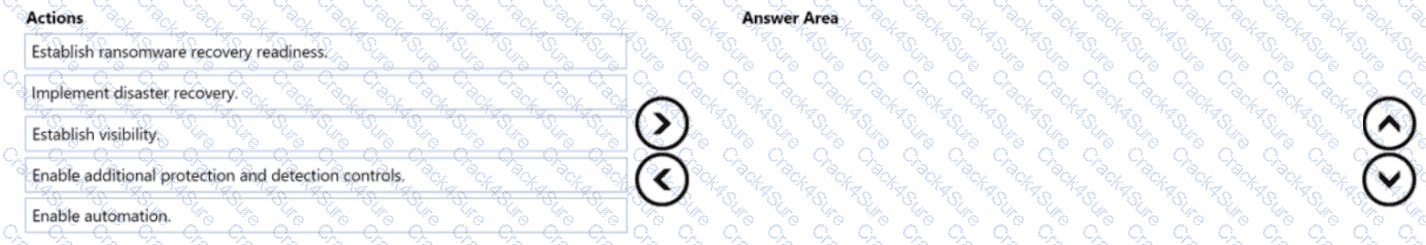
You have a Microsoft 365 subscription that syncs with Active Directory Domain Services (AD DS).
You need to define the recovery steps for a ransomware attack that encrypted data in the subscription The solution must follow Microsoft Security Best Practices.
What is the first step in the recovery plan?
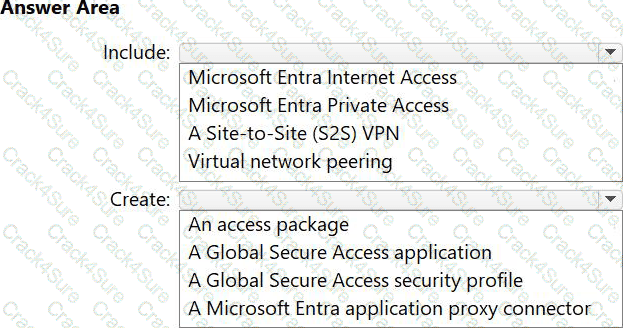
You have 500 on-premises Windows devices that are joined to a Microsoft Entra tenant named Tenant1 and enrolled in Microsoft Intune.
You have an Azure subscription named Sub1 that is linked to Tenant1.
You have a partner company that has an Azure subscription named Sub2. Sub2 contains a virtual network named VNet2 and a storage account named storage1. storage1 is secured by using an Azure Private Link endpoint on VNet2.
You need to recommend a solution to ensures that all the users at your company can access storage1 .
The solution must meet the following requirements:
• The users must sign in from a compliant device before accessing storage1.
• Access must NOT expose or provide connectivity to any other resources in Sub2.
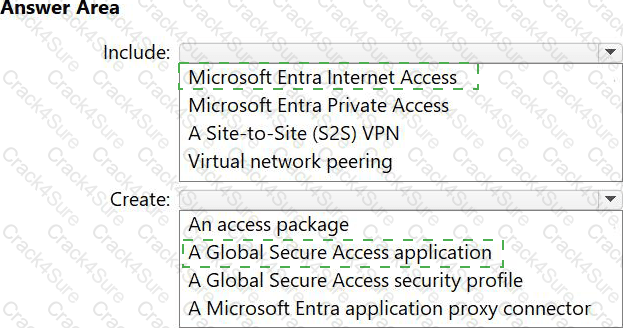
What should you include in the recommendation, and what should you recommend creating in Tenant1? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You are designing the security standards for a new Azure environment.
You need to design a privileged identity strategy based on the Zero Trust model.
Which framework should you follow to create the design?
You have an Azure subscription and an Azure DevOps organization.
You need to recommend a solution for connecting Azure DevOps pipelines to the resources in the subscription by using Azure Resource Manager (ARM) service connections. The solution must align with Microsoft Cloud Adoption Framework for Azure best practices, including the principle of least privilege.
What should you include in the recommendation?
You have an on-premises network that has several legacy applications. The applications perform LDAP queries against an existing directory service.
You are migrating the on-premises infrastructure to a cloud-only infrastructure.
You need to recommend an identity solution for the infrastructure that supports the legacy applications. The solution must minimize the administrative effort to maintain the infrastructure.
Which identity service should you include in the recommendation?
You have an Azure subscription that is linked to a Microsoft Entra tenant.
You plan deploy an enterprise application named Appl. App1 requires LDAP to look up attributes related to Microsoft Entra users.
You need to recommend a solution to support the LDAP requirement.
What should you recommend?
Your company has an Azure subscription that has enhanced security enabled for Microsoft Defender for Cloud.
The company signs a contract with the United States government.
You need to review the current subscription for NIST 800-53 compliance.
What should you do first?
You have an Azure subscription. The subscription contains multiple Azure App Service web apps that are distributed across multiple Azure regions and are accessed via the internet
You need to ensure that all incoming requests to the apps are inspected for threats based on the Core Rule Set (CRS) from the Open Web Application Security Project (OWASP). The solution must meet the following requirements:
• Support the use of Microsoft-managed X.509 certificates.
• Route users to the geographically closest app.
• Minimize administrative effort.
What should you use?
Your on-premises network contains an e-commerce web app that was developed in Angular and Nodejs. The web app uses a MongoDB database. You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.
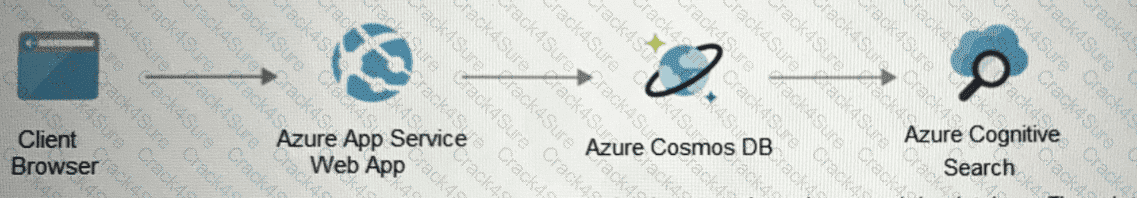
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model.
Solution: You recommend creating private endpoints for the web app and the database layer.
Does this meet the goal?
You have two Azure subscriptions named Sub1 and Sub2 that contain the vaults shown in the following table.
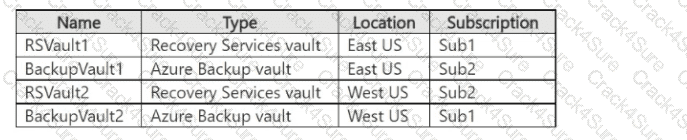
You need to design a multi-user authorization (MUA) solution for security operations on the vaults. The solution must meet the following requirements:
• RSVault1 and RSVault2 must require MUA for disabling soft delete, removing MUA protection, and disabling immutability.
• BackupVault1 and BackupVault2 must require MUA for disabling soft delete and removing MUA protection.
What is the minimum number of Resource Guard resources required?
You have a Microsoft 365 tenant named contoso.com.
You need to ensure that users can authenticate only to contoso.com. The solution must meet the following requirements:
• Prevent the users from authenticating to other Microsoft 365 tenants.
• Minimize administrative effort.
What should you use?
You need to recommend a solution to scan the application code. The solution must meet the application development requirements. What should you include in the recommendation?
You need to recommend a solution to meet the security requirements for the InfraSec group.
What should you use to delegate the access?
You need to recommend a solution to secure the MedicalHistory data in the ClaimsDetail table. The solution must meet the Contoso developer requirements.
What should you include in the recommendation?
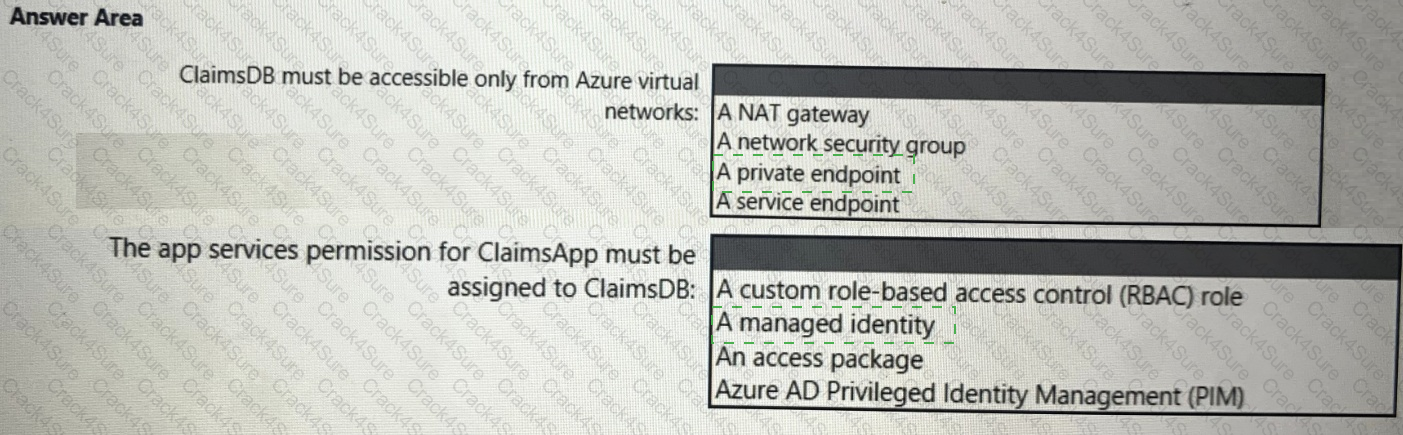
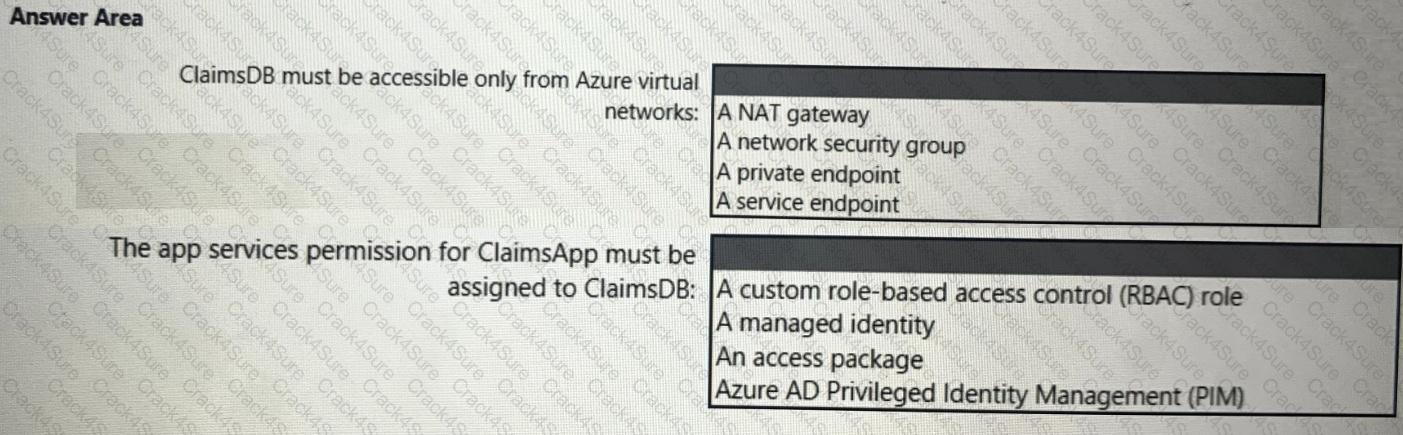
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
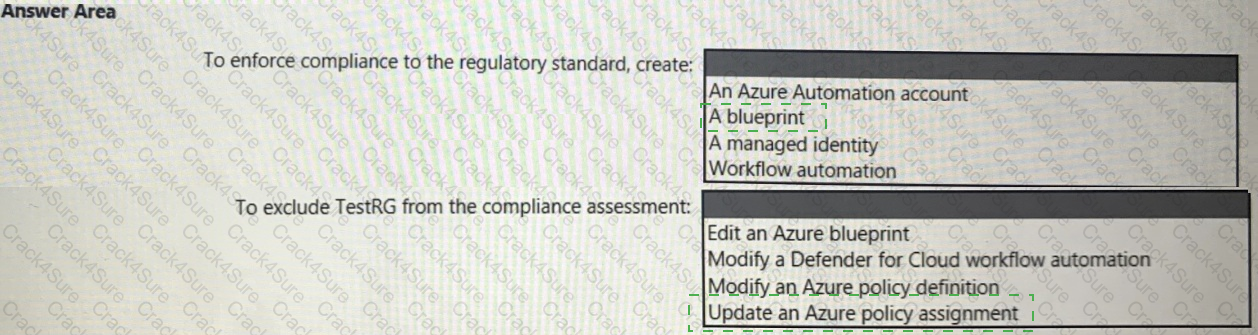
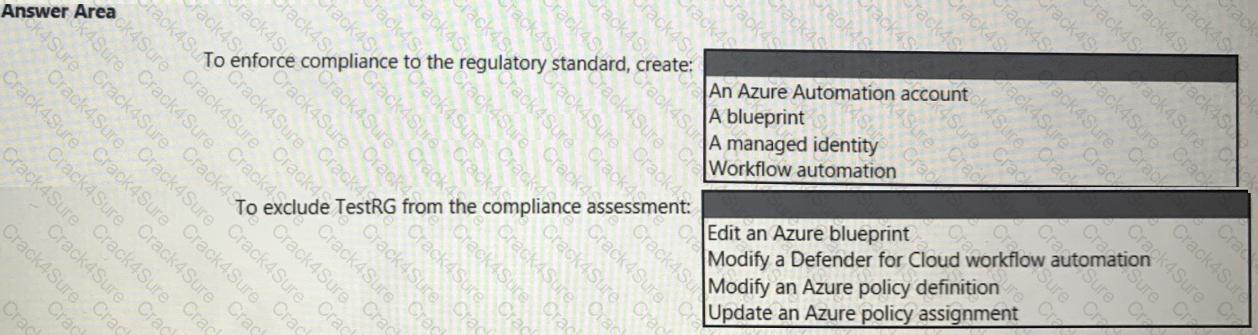
You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
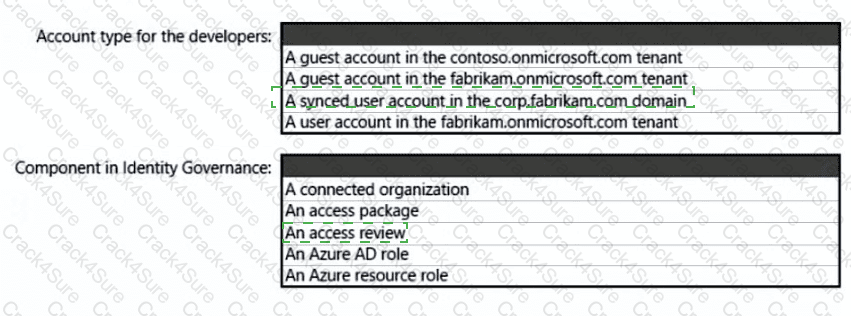
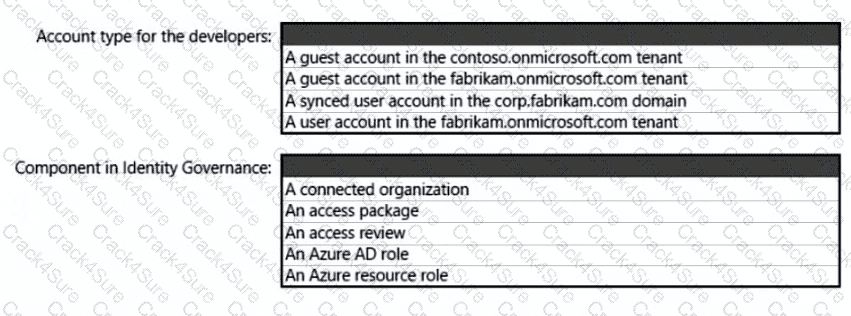
What should you create in Azure AD to meet the Contoso developer requirements?
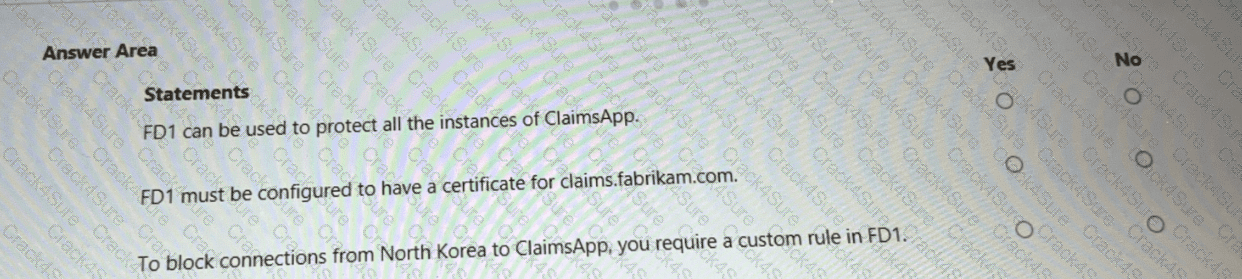
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
You need to recommend a solution to resolve the virtual machine issue. What should you include in the recommendation? (Choose Two)
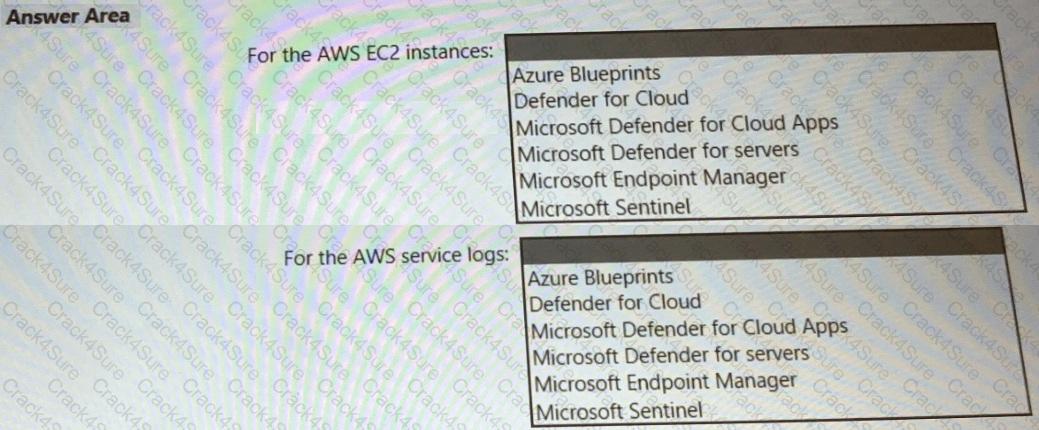
You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
3 Months Free Update
3 Months Free Update
3 Months Free Update


TESTED 12 Oct 2026