Black Friday Flash Blitz - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 75special

Practice Free GH-200 GitHub Actions Exam Exam Questions Answers With Explanation

We at Crack4sure are committed to giving students who are preparing for the Microsoft GH-200 Exam the most current and reliable questions . To help people study, we've made some of our GitHub Actions Exam exam materials available for free to everyone. You can take the Free GH-200 Practice Test as many times as you want. The answers to the practice questions are given, and each answer is explained.

Question # 6

As a DevOps engineer developing a JavaScript action, you need to include annotations to pass warning messages to workflow runners. Which code snippet can you use to implement an annotation in your Actions?

As a DevOps engineer developing a JavaScript action, you need to include annotations to pass warning messages to workflow runners. Which code snippet can you use to implement an annotation in your Actions?

A.

core.info( ' Something went wrong, but it\ ' s not bad enough to fail the build. ' )

B.

core.notice( ' Something went wrong, but it\’s not bad enough to fail the build. ' )

C.

core.warning( ' Something went wrong, but it\ ' s not bad enough to fail the build. ' )

D.

core.warn( ' Something went wrong, but it\ ' s not bad enough to fail the build. ' )

Question # 7

Which of the following is the best way for an enterprise to prevent certain marketplace actions from running?

A.

Create a list of the actions that are restricted from being used as an enterprise policy. Every other action can be run.

B.

It is not possible; if an action is in the marketplace, its use cannot be restricted.

C.

Create a list that is maintained as a . yml file in a . github repository specified in the enterprise. Only these actions can be run.

D.

Create a list of the actions that are allowed to run as an enterprise policy. Only these actions can be run.

Question # 8

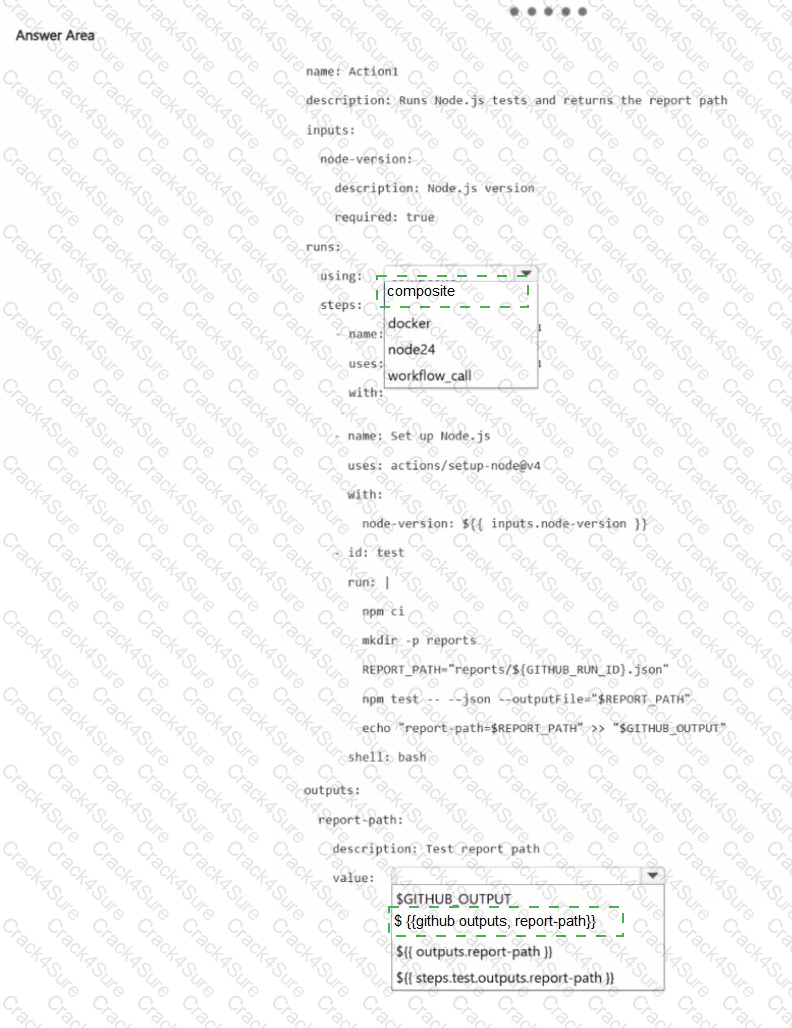
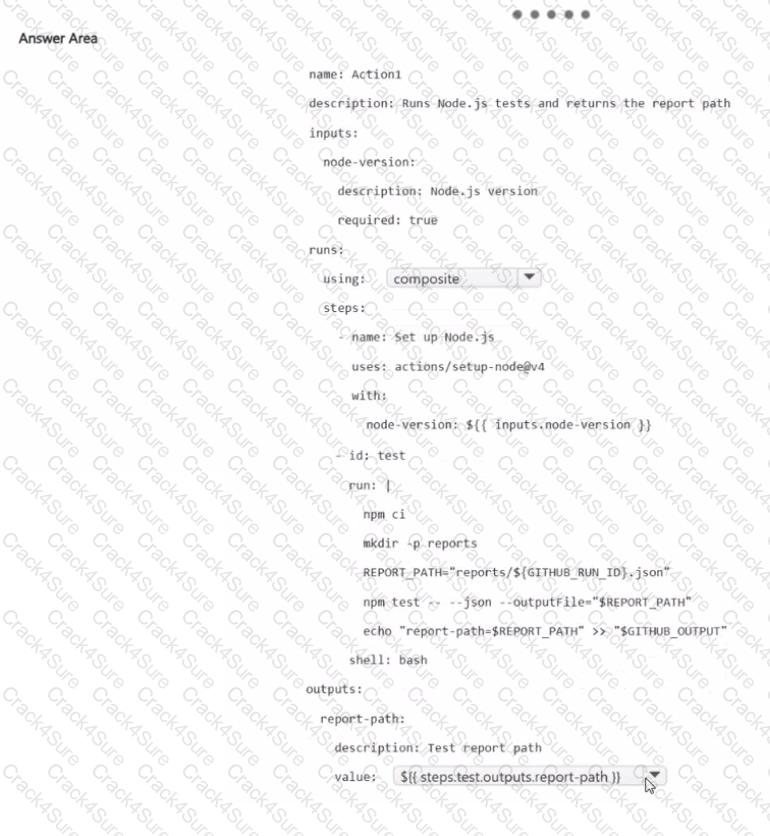
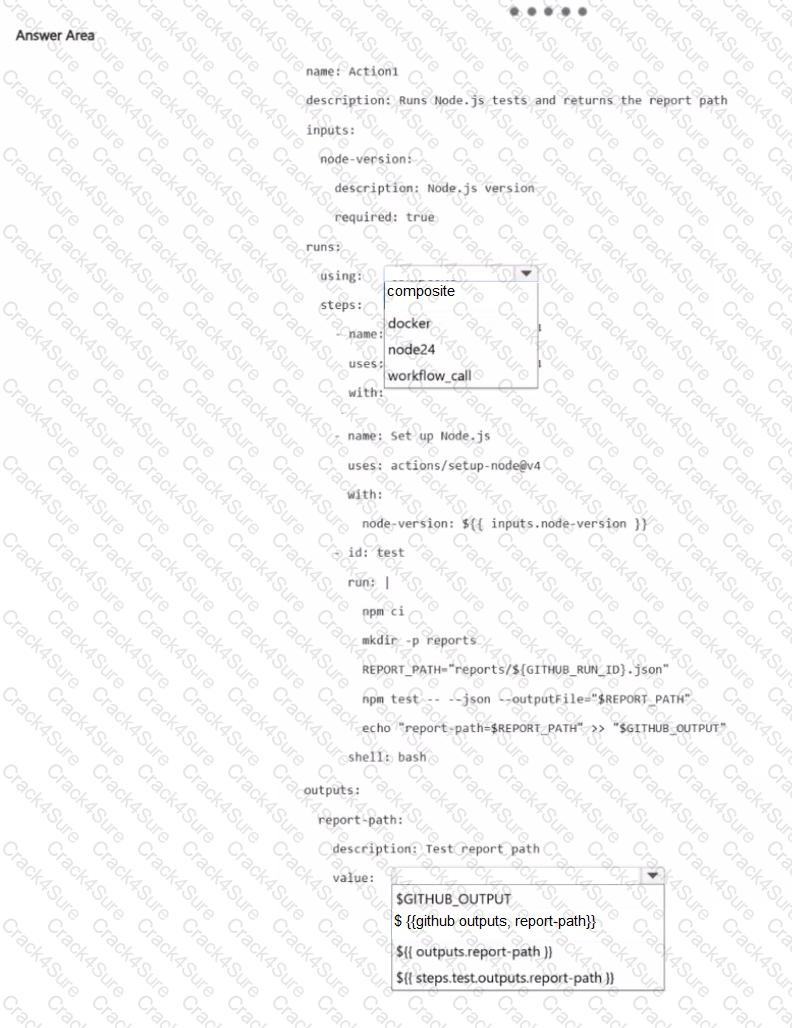
You have a GitHub repository that contains a Node.js project and a local action named Action1. Multiple jobs in repository workflows call Action1. Action1 installs dependencies, runs tests, and returns a generated report path to the calling workflows.

You need to ensure that Action1 meets the following requirements:

• Encapsulates multiple workflow steps without packaging a separate runtime

• Exposes the report path produced by the test step

How should you complete the metadata file? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.
GH-200 question answer

Question # 9

Which native method should you use to pass files between jobs within the same GitHub Actions workflow?

A.

Use artifact storage.

B.

Use job outputs.

C.

Use the copy action with the cache parameter to cache the data.

D.

Use an external blob store

Question # 10

As a developer, you need to make sure that only actions from trusted sources are available for use in your GitHub Enterprise Cloud organization. Which of the following statements are true? (Choose three.)

A.

Specific actions can individually be enabled for the organization, including version information.

B.

GitHub-verified actions can be collectively enabled for use in the enterprise.

C.

Actions can be restricted to only those available in the enterprise.

D.

Actions created by GitHub are automatically enabled and cannot be disabled.

E.

Individual third-party actions enabled with a specific tag will prevent updated versions of the action from introducing vulnerabilities.

F.

Actions can be published to an internal marketplace.

Question # 11

As a developer, you have a 10-MB data set that is required in a specific workflow. Which steps should you perform so the dataset is stored encrypted and can be decrypted during the workflow? (Choose three.)

A.

Encrypt the dataset.

B.

Leverage the actions/download-secret action in the workflow.

C.

Store the dataset in a GitHub encrypted secret.

D.

Store the encryption keys in a GitHub encrypted secret.

E.

Compress the dataset

F.

Commit the encrypted dataset to the same repository as the workflow

G.

Create a GitHub encrypted secret with the Large object option selected and upload the dataset.

Question # 12

Which statement is true about using default environment variables?

A.

The environment variables can be read in workflows using the ENV: variable_name syntax.

B.

The environment variables created should be prefixed with GITHUB_ to ensure they can be accessed in workflows

C.

The environment variables can be set in the defaults: sections of the workflow

D.

The GITHUB_WORKSPACE environment variable should be used to access files from within the runner.

Question # 13

Which of the following is a valid reusable workflow reference?

A.

uses: another-repo/workflow.yml@v1

B.

uses: octo-org/another-repo/.github/workflows/workflow.yml@v1

C.

uses: octo-org/another-repo/workflow.yml@v1

D.

uses: another-repo/.github/workflows/workflow.yml@v1

Question # 14

You need to make a script to retrieve workflow run logs via the API. Which is the correct API to download a workflow run log?

A.

POST /repos/:owner/:repo/actions/runs/:run_id

B.

GET /repos/:owner/:repo/actions/artifacts/logs

C.

GET /repos/:owner/:repo/actions/runs/:run_id/logs

D.

POST /repos/:owner/:repo/actions/runs/:run_id/logs

Question # 15

You create a self-hosted runner labeled as runner1.

You need to ensure that a GitHub Actions workflow job runs only on runner1.

Which YAML statement should you use?

A.

runs-on: [self-hosted, linux-xlarge]

B.

runs-on: - self-hosted - ubuntu-latest

C.

runs-on: [self-hosted, runner1]

D.

runs-on: self-hosted

Question # 16

What are the two types of environment protection rules you can configure? (Choose two.)

A.

required reviewers

B.

branch protections

C.

wait timer

D.

artifact storage

Question # 17

You need to create a reusable GitHub Actions workflow template named ci.yml. The solution must ensure that ci.yml appears on the New workflow interface of GitHub Actions. Where should you store ci.yml?

A.

.github/workflows

B.

.github/templates

C.

.github/workflow-templates

D.

the root directory of each repository

Question # 18

What metadata file in a custom action defines the main entry point?

A.

action.js

B.

index.js

C.

action.yml

D.

main.yml

Question # 19

You are a developer working on developing reusable workflows for your organization. What keyword should be included as part of the reusable workflow event triggers?

A.

check_run

B.

pull_request

C.

workflow_run

D.

workflow_call

Question # 20

As a developer, you are authoring a workflow that will deploy to both DevCloud and TestCloud resources. Each cloud resource is accessed with a different deployment key. Which approach best allows you to use the same reusable workflow in separate jobs to target the different cloud resources?

A.

Create repository secrets named DevCloud.DEPLOY_KEY and TestCloud.DEPLOY_KEY so that the reusable workflow parses the secrets by resource name.

B.

Store the different keys in a DEPLOY_KEY environment secret in the DevCloud and TestCloud environments. Specify DEPLOY_KEY in the secrets section of the reusable workflow.

C.

Use a marketplace action to conditionally parse the DEPLOY_KEY repository secret based on the cloud resource name.

D.

Populate a DEPLOY_KEY repository secret with a JSON object containing DevCloud and TestCloud properties. Then specify DEPLOY_KEY.DevCloud in the secrets sections of the reusable workflow.

Question # 21

Custom environment variables can be defined at multiple levels within a workflow file, including which three levels?

(Each correct answer presents a complete solution. Choose three.)

A.

Stage level

B.

Default level

C.

Step level

D.

Runner level

E.

Top level

F.

Job level

Question # 22

As a developer, how can you identify a Docker container action on GitHub?

A.

The action ' s repository includes @actions/core in the root directory.

B.

The action ' s repository name includes the keyword " Docker. "

C.

The action.yml metadata file references a Dockerfile file.

D.

The action.yml metadata file has the runs.using value set to Docker.

Question # 23

When reviewing an action for use, what file defines its available inputs and outputs?

A.

inputs.yml

B.

config.json

C.

defaults.json

D.

workflow.yml

E.

action.yml

Question # 24

As a DevOps engineer, you are developing a composite action. You have a step that needs to be executed against a subdirectory. Which code snippet should you use within the composite action to specify the directory?

A.

runs: using: " composite " steps: - run: $GITHUB_ACTION_PATH/script.sh directory: ${{ inputs.dir }} shell: bash

B.

runs: using: " composite " steps: - run: $GITHUB_ACTION_PATH/script.sh working-directory: ${{ inputs.dir }} shell: bash

Question # 25

In which of the following scenarios should you use self-hosted runners? Each correct answer presents a complete solution.

NOTE: Each correct answer is worth one point.

A.

when the workflow jobs must be run on Windows 10

B.

when jobs must run for longer than 6 hours

C.

when you want to use macOS runners

D.

when GitHub Actions minutes must be used for the workflow runs

E.

when a workflow job needs to install software from the local network

Question # 26

In which scenarios could the GITHUB_TOKEN be used? (Choose two.)

A.

to leverage a self-hosted runner

B.

to create a repository secret

C.

to publish to GitHub Packages

D.

to create issues in the repo

E.

to read from the file system on the runner

F.

to add a member to an organization

Question # 27

Which action type should be used to bundle a series of run steps into a reusable custom action?

A.

Composite action

B.

Bash script action

C.

Docker container action

D.

JavaScript action

Question # 28

You need to use a specific version of an action. How should you use v1 of an actions/javascript-action repository in your workflow?

A.

steps:uses: actions/javascript-action/v1

B.

steps:uses: actions/javascript-actionversion: v1

C.

steps:uses: actions/javascript-action-v1

D.

steps:uses: actions/javascript-action@v1

Question # 29

What will the output be for the following event trigger block in a workflow?

A.

It throws a workflow syntax error, pointing to the types definition in issue_comment event.

B.

It throws a workflow syntax error, pointing to the types definition in issues event.

C.

It runs the workflow when an issue is edited or when an issue comment created.

D.

It runs the workflow when an issue or issue comment in the workflow ' s repository is created or modified.

E.

It runs the workflow when an issue is created or edited, or when an issue or pull request comment is created.

Question # 30

Which statement is true regarding the ability to delete a workflow run?

A.

Completed workflow runs may be deleted.

B.

Pending workflow runs may be deleted.

C.

Workflow runs must be older than 30 days to be deleted.

D.

Admin access is required to delete a workflow run.

Question # 31

As a developer, how can you identify a composite action on GitHub?

A.

The action’s repository includes Dockerfile and package.json files.

B.

The action.yml metadata file has the runs.using value set to composite.

C.

The action’s repository name includes the keyword “composite.”

D.

The action’s repository includes an init.sh file in the root directory.

Question # 32

What is the most secure way to store sensitive information in GitHub Actions workflows?

A.

Use environment variables in the workflow and store sensitive data directly in the variables.

B.

From the GitHub repository settings, store sensitive data as unencrypted text.

C.

Store the sensitive information as plain text in the workflow YAML file.

D.

Use GitHub Enterprise Managed User (OIDC) integration to dynamically fetch secrets from a third-party secrets manager.

Question # 33

What are the two mandatory requirements for publishing GitHub Actions to the GitHub Marketplace? Each correct answer presents part of the solution.

NOTE: Each correct answer is worth one point.

A.

The action can be either in a public or private repository.

B.

The action’s name cannot match a user or organization on GitHub unless the user or organization owner is publishing the action.

C.

Each repository can contain a collection of actions as long as they are under the same Marketplace category.

D.

The action’s metadata file must be in the root directory of the repository.

E.

The name should match with one of the existing GitHub Marketplace categories.

Question # 34

As a DevOps engineer, you need to execute a deployment to different environments such as development and testing based on labels added to a pull request. The deployment should use the releases branch and trigger only when there is a change in files under the apps folder. Which code block should be used to define the deployment workflow trigger?

A.

on: pull_request_review: types: [labeled] branches: - ' releases ' paths: - ' apps/** '

B.

on: pull_request: types: [labeled] branches: - ' releases/** ' paths: - ' apps '

C.

on: pull_request: types: [labeled] branches: - ' releases ' paths: - ' apps/** '

D.

on: pull_request_label: branches: - ' releases ' paths: - ' apps/** '

Question # 35

You are a DevOps engineer working on deployment workflows. You need to execute the deploy job only if the current branch name is feature-branch. Which code snippet will help you implement the conditional execution of the job?

A.

jobs: deploy: if: github.branch_name == ' feature-branch ' runs-on: ubuntu-latest

B.

jobs: deploy: if: github.ref_name == ' feature-branch ' runs-on: ubuntu-latest

C.

jobs: deploy: if: github.ref.name = ' feature-branch ' runs-on: ubuntu-latest

D.

jobs: deploy: if: github.branch.name == ' feature-branch ' runs-on: ubuntu-latest

Question # 36

You are a DevOps engineer in ABC Corp. You need to schedule your deployment workflow twice a week at 7:45 UTC every Wednesday and Saturday. What is the appropriate YAML structure?

A.

on: schedule: - cron: ' 45 7 * * 3,6 '

B.

on: cron: - schedule: ' 45 7 * * 3,6 '

C.

on: schedule: ' 45 7 * * 3,6 '

D.

on: cron: ' 45 7 * * 3,6 '

Question # 37

You are a developer, and your container jobs are failing on a self-hosted runner. Which requirements must you check to ensure that the self-hosted runner is properly configured? (Choose two.)

A.

The self-hosted runner is running a Linux operating system.

B.

The self-hosted runner is running a Windows operating system.

C.

Docker is installed on the self-hosted runner.

D.

Kubernetes is installed on the self-hosted runner.

E.

The service status of Kubernetes is " active " .

Question # 38

As a developer, how should you enable step debug logging for a workflow?

A.

Include the following code block in your workflow:defaults: ACTIONS_STEP_DEBUG: true

B.

Use the --actions-step-debug flag when calling the workflow.

C.

Set the ACTIONS_STEP_DEBUG secret or variable at the repository level to true.

D.

Include the following code block in your workflow:env: ACTIONS_STEP_DEBUG: true

Question # 39

As a developer, your Actions workflow often reuses the same outputs or downloaded dependencies from one run to another. To cache dependencies for a job, you are using the GitHub cache action. Which input parameters are required for this action? (Choose two.)

A.

dependency: the name and version of a package to cache or restore

B.

key: the key created when saving a cache and the key used to search for a cache

C.

cache-hit: the copy action key used with restore parameter to restore the data from the cache

D.

path: the file path on the runner to cache or restore

E.

ref: the ref name of the branch to access and restore a cache created

F.

restore-keys: the copy action key used with cache parameter to cache the data

Question # 40

Which workflows can use an action stored in an internal repository when repository access is enabled for the organization or enterprise?

(Each correct answer presents a complete solution. Choose two.)

A.

Workflows in internal repositories owned by the same organization or enterprise.

B.

Workflows in private repositories owned by an organization in the enterprise.

C.

Workflows in selected public repositories outside the enterprise.

D.

Workflows in public repositories owned by the same organization as the enterprise.

Question # 41

As a developer, you need to create a custom action written in Python. Which action type should you choose?

As a developer, you need to create a custom action written in Python. Which action type should you choose?

A.

JavaScript action

B.

composite run step

C.

Python action

D.

Docker container action

Question # 42

Which run: command will set a step ' s output?

A.

run: echo " MY_OUTPUT=foo " > > $GITHUB_OUTPUT

B.

run: export MY_OUTPUT=foo

C.

run: echo ${{ $GITHUB_OUTPUT=foo }}

D.

run: echo " ::set-env name=MY OUTPUT::foo "

Question # 43

You are a DevOps engineer working on custom Actions development. You need to handle the errors or exceptions as part of the JavaScript-based action code. What should be added to the following code block to handle errors?

Exhibit:

const core = require( ' @actions/core ' );

try {

// action code

} catch (error) {

< < insert snippet here > >

}

A.

core.action.setException(error.Message);

B.

action.setError(error.Message);

C.

core.setFailed(error.Message);

D.

core.setException(error.message);

Question # 44

How can GitHub Actions encrypted secrets be used in if: conditionals within a workflow job?

A.

Set the encrypted secret as a job-level environment variable and then reference the environment variable within the conditional statement.

B.

Create a job dependency that exposes the encrypted secret as a job output, which can then be leveraged in a subsequent dependent job.

C.

Use the secrets context within the conditional statement, e.g. ${{ secrets.MySuperSecret }}.

D.

Use a workflow command to expose the encrypted secret via a step ' s output parameter and then use the step output in the job ' s if: conditional.

Question # 45

Which choices represent best practices for publishing actions so that they can be consumed reliably?

(Each correct answer presents a complete solution. Choose two.)

A.

Organization name

B.

Commit SHA

C.

Repository name

D.

Tag

E.

Default branch

GH-200 PDF

$35

$139.99

3 Months Free Update

  • Printable Format
  • Value of Money
  • 100% Pass Assurance
  • Verified Answers
  • Researched by Industry Experts
  • Based on Real Exams Scenarios
  • 100% Real Questions

GH-200 PDF + Testing Engine

$47.5

$189.99

3 Months Free Update

  • Exam Name: GitHub Actions Exam
  • Last Update: Nov 20, 2026
  • Questions and Answers: 150
  • Free Real Questions Demo
  • Recommended by Industry Experts
  • Best Economical Package
  • Immediate Access

GH-200 Engine

$40

$159.99

3 Months Free Update

  • Best Testing Engine
  • One Click installation
  • Recommended by Teachers
  • Easy to use
  • 3 Modes of Learning
  • State of Art Technology
  • 100% Real Questions included