Crack4sure Logo
We at Crack4sure are committed to giving students who are preparing for the Splunk SPLK-5002 Exam the most current and reliable questions . To help people study, we've made some of our Splunk Certified Cybersecurity Defense Engineer exam materials available for free to everyone. You can take the Free SPLK-5002 Practice Test as many times as you want. The answers to the practice questions are given, and each answer is explained.
Which of the following actions will allow access to a list of alert actions via the API?
A cyber defense engineer plays a role in maintaining a secure SOAR Cloud configuration. Which network security statement is correct about SOAR Cloud?
Consider the following series of events:
4:00 GMT Detection runs for interval 3:30–4:00
4:30 GMT Detection runs for interval 4:00–4:30
4:35 GMT Event 1 occurs on an endpoint
4:45 GMT Event 1 is indexed
5:00 GMT Detection runs for interval 4:30–5:00
5:05 GMT Event 1 finding is added to ES with timestamp 4:35
5:24 GMT Event 2 occurs on an endpoint
5:30 GMT Detection runs for interval 5:00–5:30
5:35 GMT Event 2 is indexed
6:00 GMT Detection runs for interval 5:30–6:00
What is the problem with the detection schedule chosen and how can it be solved?
When creating a detection that searches user activity across CIM-compliant data, which CIM field should be reviewed to ensure that data is aggregated appropriately?
Which Splunk feature makes SPL searches shorter and reusable by inserting it into search strings?
A Splunk administrator needs to integrate a third-party vulnerability management tool to automate remediation workflows. What is the most efficient first step?
There are multiple methods for communicating data with a REST endpoint. In the URL shown, what is the name of the key-value pairs represented after the question mark in the URL?
Which field in the risk index is used to describe the activity within a finding?
The following SPL is designed to report on a certain SOC metric. Which metric is the most likely topic for this report?
| tstats summariesonly=true earliest(_time) as _time
FROM datamodel=Incident_Management
BY " Notable_Events.Meta.rule_id "
| rename " Notable_Events.Meta.* " as " * "
| lookup update=true incident_updates_lookup rule_id OUTPUTNEW time
| search time=*
| stats earliest(_time) as create_time, min(time) as triage_time by rule_id
| eval diff=triage_time-create_time,
stat_type=if(
create_time < relative_time(now(), " -7d@d " ),
" past " ,
" current "
),
past=if(stat_type= " past " , 1, 0),
current=if(stat_type= " current " , 1, 0),
past_diff=if(stat_type= " past " , diff, 0),
current_diff=if(stat_type= " current " , diff, 0)
| stats sum(past) AS past,
sum(current) AS current,
sum(past_diff) AS past_diff,
sum(current_diff) AS current_diff
| eval past=round(past_diff/past/60),
current=round(current_diff/current/60)
| table past, current
| transpose
In Enterprise Security, what is the name of the threat intelligence lookup pertaining to files?
An engineer is writing a correlation search and needs to use T1059 from MITRE ATT & CK as a field in Incident Review. Assuming they are writing a correlation search that does not use the Risk data model, which example statement should be appended to the correlation search?
When creating a case in Splunk SOAR, which action should be taken to correlate various findings (risk notables) to ensure all are actioned?
Which action improves the effectiveness of notable events in Enterprise Security?
When building detections using the Authentication Data Model, which values are recommended for use against the action field?
In order to perform a complete data assessment, an engineer ' s role within Splunk must have which of the following?
Which of the following is a reason to utilize ES risk framework as a part of detection building?
Which of the following detections would use a high count of events with Windows Event Code 4740 grouped by a user to determine suspicious behavior?
Which of the following should an engineer do as they evaluate their Threat Detection and Incident Response lifecycle?
During a ransomware attack, an adversary might add a default user and password in registry, modify the wallpaper, and create bulk ransomware notes across multiple machines. What is Splunk ' s method for grouping these types of detections together?
If a correlation search cannot be run at the configured time, which scheduling option should an engineer use to ensure there are no backfill gaps in data?
How can you incorporate additional context into notable events generated by correlation searches?
What is the primary purpose of data indexing in Splunk?
An engineer notices that a detection is creating multiple Findings (notables) for the same potential incident. Which setting can be adjusted to reduce the number of generated findings (notables)?
What should a security engineer prioritize when building a new security process?
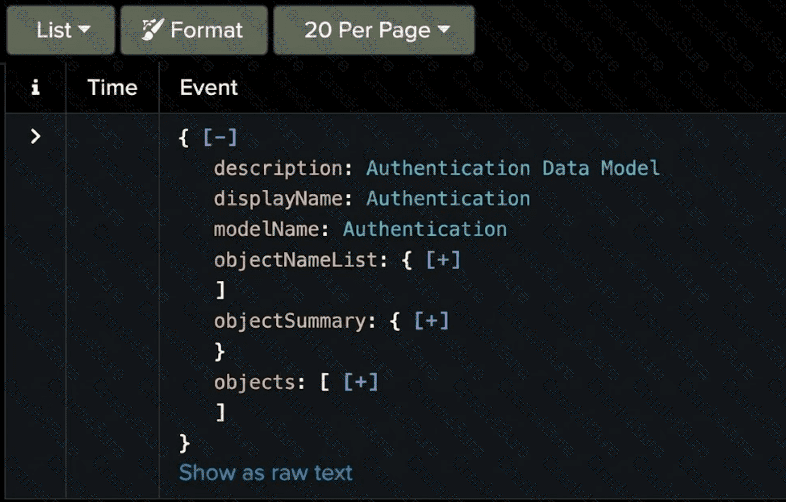
Which search command was used to generate the result in the image below?
Which stats event field created by an adaptive response action allows for troubleshooting the correlation search that created the notable event?
3 Months Free Update
3 Months Free Update
3 Months Free Update


TESTED 17 Oct 2026